Настройка VPN в Hive OS
такая же шляпа.
служба поддержки вот так послала меня:
I’m afraid we don’t have the application for Hive OS, as this operating system isn’t supported,
but you can set up a VPN connection on your router, which would make your Hive OS device be connected to a VPN as well!
вот такие пироги.
Кто какой VPN использует для HIVE?
Поднять свой не предлагать
dio199
Бывалый
- 12 Апр 2022
- #62
такая же шляпа.
служба поддержки вот так послала меня:
I’m afraid we don’t have the application for Hive OS, as this operating system isn’t supported,
but you can set up a VPN connection on your router, which would make your Hive OS device be connected to a VPN as well!
вот такие пироги.
Кто какой VPN использует для HIVE?
Поднять свой не предлагать
d_bagrov
Знающий
- 12 Апр 2022
- #63
d_bagrov
Знающий
- 12 Апр 2022
- #64
| push-remove ifconfig-ipv6 push-remove route-ipv6 |
Oceanov
Свой человек
- 15 Апр 2022
- #65
Bodybag
Пляшущий с бубном
- 21 Апр 2022
- #66
| push-remove ifconfig-ipv6 push-remove route-ipv6 |
Подскажите где поколдовать в файле, на винде все отлично завелось в хайве делает мозги "OpenVPN setup failed"
dev tun
fast-io
persist-key
persist-tun
nobind
remote "server ip"
remote-random
pull
comp-lzo no
tls-client
verify-x509-name Server name-prefix
ns-cert-type server
key-direction 1
route-method exe
route-delay 2
tun-mtu 1500
fragment 1300
mssfix 1200
verb 3
cipher AES-256-CBC
keysize 256
auth SHA512
sndbuf 524288
rcvbuf 524288
auth-user-pass
Oceanov
Свой человек
- 23 Апр 2022
- #67
Подскажите где поколдовать в файле, на винде все отлично завелось в хайве делает мозги "OpenVPN setup failed"
dev tun
fast-io
persist-key
persist-tun
nobind
remote "server ip"
remote-random
pull
comp-lzo no
tls-client
verify-x509-name Server name-prefix
ns-cert-type server
key-direction 1
route-method exe
route-delay 2
tun-mtu 1500
fragment 1300
mssfix 1200
verb 3
cipher AES-256-CBC
keysize 256
auth SHA512
sndbuf 524288
rcvbuf 524288
auth-user-pass
SSL configuration in Hive
You can configure SSL by one of the following methods:
- upload your SSL certificates to the Platform and configure HTTP-to-HTTPS redirect or HTTPS-only;
- configure HTTP or TCP Reverse proxy with SSL termination.
Upload SSL certificates to Hive
Upload SSL certificates in the PEM format to the directory /opt/hw-bw/ssl . Please note that uploaded files will not be overwritten when upgrading to the next version, so feel free to store them on the Platform.
You can change default directory if it does not suit you:
-
Open the file /opt/hw-bw/config/user.ini (root privileges required);
Add the b.ssl.dir option to the [main] section and indicate new path:
To apply changes, run the command:
Configure HTTP-to-HTTPs redirect or HTTPs-only
To configure HTTP-to-HTTPs redirect or HTTPs-only, perform the following steps:
-
Open the file /opt/hw-bw/config/user.ini (root privileges required);
Add the following options to the [main] section:
b.ssl.enabled — option, which enables SSL. Possible values:
- no_ssl — only insecure HTTP-connection is used (set by default);
- ssl_both — both insecure HTTP-connection and secure HTTPs-connection are used;
- ssl_redirect — redirection from insecure connection HTTP-connection to secure HTTPs-connection;
- ssl_only — only secure HTTPs-connection is used.
b.deck.ip.expose — IP address for insecure HTTP-connection ( 0.0.0.0 — public IP address, 127.0.0.1 — local IP address);
Additionally, you can add the following options:
- b.deck.https.ip.expose — IP address for secure HTTPs-connection;
- b.deck.https.port.expose — Port number for secure HTTPs-connection;
To apply changes, run the command:
Configure HTTP or TCP Reverse proxy with SSL termination
Configure proxy server before installation of the Hive. For example, configure nginx , which will proxy all requests for Hive.
To install your proxy server on the same virtual machine, change the following parameters in /opt/hw-bw/config/user.ini :
To apply changes, run the command (root privileges required):
Example of nginx configuration as HTTP Reverse proxy
Example of nginx configuration:
- 10002 — port number of your virtual machine;
- yourhive.example.com — hostname or IP address of your virtual machine.
Example of Let’s Encrypt with certbot configuration. You should set this configuration before you issue certificates using certbot .
- 10002 — port number of your virtual machine;
- yourhive.example.com — hostname or IP address of your virtual machine.
Convert CA-certificate from .PFX
You may need to convert CA from .pfx if: * it is necessary to transfer issues between Hive and Apiary via secure channel; * it is impossible to use global valid certificates; * it is necessary to use local Certificate Authority to issue certificates.
- Create SSL key:
- Create SSL certificate:
Note: remove the -out option from the commands and the key with other information will be displayed on the screen. In this case, copy everything from the lines BEGIN PRIVATE KEY / BEGIN CERTIFICATE to END PRIVATE KEY / END CERTIFICATE and save it to a file.
- Create a root certificate:
Note: you will get a chain of root certificates. You will need only last one certificate in this chain. For example, you can open file for editing and delete everything except the last one.
Tls в hive os что это
такая же шляпа.
служба поддержки вот так послала меня:
I’m afraid we don’t have the application for Hive OS, as this operating system isn’t supported,
but you can set up a VPN connection on your router, which would make your Hive OS device be connected to a VPN as well!
вот такие пироги.
Кто какой VPN использует для HIVE?
Поднять свой не предлагать
dio199
Бывалый
- 12 Апр 2022
- #62
такая же шляпа.
служба поддержки вот так послала меня:
I’m afraid we don’t have the application for Hive OS, as this operating system isn’t supported,
but you can set up a VPN connection on your router, which would make your Hive OS device be connected to a VPN as well!
вот такие пироги.
Кто какой VPN использует для HIVE?
Поднять свой не предлагать
d_bagrov
Знающий
- 12 Апр 2022
- #63
d_bagrov
Знающий
- 12 Апр 2022
- #64
Oceanov
Свой человек
- 15 Апр 2022
- #65
Bodybag
Пляшущий с бубном
- 21 Апр 2022
- #66
Подскажите где поколдовать в файле, на винде все отлично завелось в хайве делает мозги "OpenVPN setup failed"
dev tun
fast-io
persist-key
persist-tun
nobind
remote "server ip"
remote-random
pull
comp-lzo no
tls-client
verify-x509-name Server name-prefix
ns-cert-type server
key-direction 1
route-method exe
route-delay 2
tun-mtu 1500
fragment 1300
mssfix 1200
verb 3
cipher AES-256-CBC
keysize 256
auth SHA512
sndbuf 524288
rcvbuf 524288
auth-user-pass
Oceanov
Свой человек
- 23 Апр 2022
- #67
Подскажите где поколдовать в файле, на винде все отлично завелось в хайве делает мозги "OpenVPN setup failed"
dev tun
fast-io
persist-key
persist-tun
nobind
remote "server ip"
remote-random
pull
comp-lzo no
tls-client
verify-x509-name Server name-prefix
ns-cert-type server
key-direction 1
route-method exe
route-delay 2
tun-mtu 1500
fragment 1300
mssfix 1200
verb 3
cipher AES-256-CBC
keysize 256
auth SHA512
sndbuf 524288
rcvbuf 524288
auth-user-pass
Майнеру на заметку — настраиваем соединение HiveOS через VPN
Все мы понимаем, что санкции коснулись всех и каждого, в том числе и честных майнеров. В последнее время, пошла мода, добавлять «закладки» в программное обеспечение для тех, у кого российские IP адреса, примеров много — в том числе и в программы для майнинга — «майнеры». Сегодня я столкнулся с такой вот проблемой на примере майнера Wildrig-multi.
Поэтому сегодня я вкратце расскажу, как настроить сквозное соединение через VPN на примере всеми нами любимой HiveOS.
Первым делом идем на любой сайт, где есть открытые VPN сервера. Для небольших майнеров я бы посоветовал сервера на сайте https://www.vpngate.net/en/ (не реклама, сайт довольно популярный). Если кто серьезно переживает, что большой брат следит, то выбирайте платные сервера OpenVPN — яндексим усиленно!
Выбираем тот, где есть галочка на OpenVPN
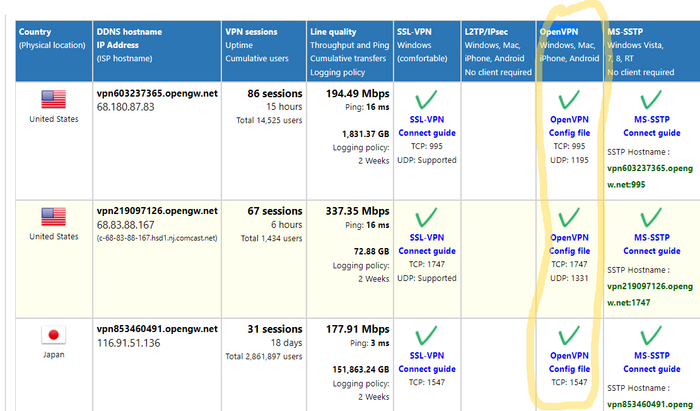
Далее нажимаем на «OpenVPN Config file» и на странице качаем файл конфигурации. Рекомендую качать файл в верхней части где содержится DDNS имя, качайте и TCP и UDP если такой имеется, если вдруг один не заработает, подкините другой.
Скачали? отлично, идем дальше, осталось всего лишь пару шагов для поднятия VPN на хайве.
Далее переходим к ферме, выбираем нашего воркера и тапаем вот сюда вот:

Открывается конфигурация клиента, здесь активируем переключатель в верхней части, выбираем наш ранее скачанный файл с сохраненной конфигурацией.
После того, как файл подгрузился, в нижнем поле указываем Логин и пароль :
Они одинаковые почти для всех серверов на данном сайте.
Все, после применения конфигурации, Хайв сообщит, что применение конфигурации прошло успешно!
На панели Вы увидите, что появился новый значок в статусе воркера, а так же внизу страницы, он говорит о том, что VPN работает, и все у нас будет если не отлично, то уж точно хорошо!

На этом все, я надеюсь данная информация будет полезна не только новичкам, но и старожилам!
Name already in use
hiveon-kb / guides / openvpn.md
- Go to file T
- Go to line L
- Copy path
- Copy permalink
Copy raw contents
Copy raw contents
The First Tutorial
This is how to check the client’s service status on the rig when you upload config and it’s not working:
Just to give you a valid example of the working config: /etc/openvpn/server.conf
And the most important — client.conf. It should go with certificate files.
Please note that in config certificates should be named as in the example:
You can upload files with any names, but then they will be renamed to ca.crt, client.crt, client.key. In this way you will have one config for all rigs.
Also you can embed your certificates into one file to client.conf, so your file will look like this:
Also if you want TLS Auth, you can embed that key in this way:
auth-user-pass is now supported also. So just put this option in client config and upload it with giving login and password in upload dialog.
The Second Tutorial
First of all you need to have a PC or a Server that needs to have a fixed IP on the internal network (the network where you host the VPN Server). Please remember that all VPN traffic will go to the VPN Server machine, coming from each VPN client (each of your rigs and yourself at your personal computer).
We’re assuming you already have installed your VPN Server software at your Windows or Linux. Please note that OpenVPN 2.4 installers will not work on Windows XP.
If you use, for example, Debian, to install OpenVPN just type: apt-get install openvpn . With this you get the Debian OpenVPN package that you will use to set up your OpenVPN server and generate server and client keys.
Links to download OpenVPN and install it manually at the time this tutorial was written:
First we need to create the CA certificate. To do this use the following commands:
If you are using Linux, BSD, or a Unix-like OS, open a shell and use the cd command to go to the easy-rsa subdirectory. If you installed OpenVPN from an RPM or DEB file, the easy-rsa subdirectory can usually be found in /usr/share/doc/packages/openvpn or /usr/share/doc/openvpn (it’s best to copy this directory to another location such as /etc/openvpn, before any edits, so that future OpenVPN package upgrades won’t overwrite your modifications). If you installed from a .tar.gz file, the easy-rsa subdirectory will be in the top level directory of the expanded source tree.
At Debian, if you did apt-get install openvpn , execute the following commands:
If you are using Windows, open up a Command Prompt window and use cd to get to \Program Files\OpenVPN\easy-rsa. Run the following batch file to copy configuration files into place (this will overwrite any preexisting vars.bat and openssl.cnf files): init-config .
Now edit the vars file (called vars.bat on Windows / at Linux use the pico vars command) and set the KEY_COUNTRY, KEY_PROVINCE, KEY_CITY, KEY_ORG, and KEY_EMAIL parameters. Don’t leave any of these parameters blank:
Set KEY_SIZE to “4096”
Exit and save the vars file.
At Debian, if you did apt-get install openvpn , run this command: cp openssl-1.0.0.cnf openssl.cnf .
Next, initialize the PKI.
Next, we will generate a certificate and private key for the server.
On Linux/BSD/Unix: ./build-key-server server .
On Windows: build-key-server server .
As in the previous step, most parameters can be defaulted. When the Common Name is queried, enter “server”. Two other queries require positive responses, “Sign the certificate? [y/n]” and “1 out of 1 certificate requests certified, commit? [y/n]”.
Generate certificates & keys for 3 clients. Generating client certificates is very similar to the previous step.
Remember that for each client, make sure to type the appropriate Common Name when prompted, i.e. “client1”, “client2”, or “client3”. Always use a unique common name for each client.
Generate Diffie Hellman parameters
Diffie Hellman parameters must be generated for the OpenVPN server.
On Linux/BSD/Unix: ./build-dh
On Windows: build-dh
Now we will find our newly-generated keys and certificates in the keys subdirectory (my_ca/keys). Here is an explanation of the relevant files:
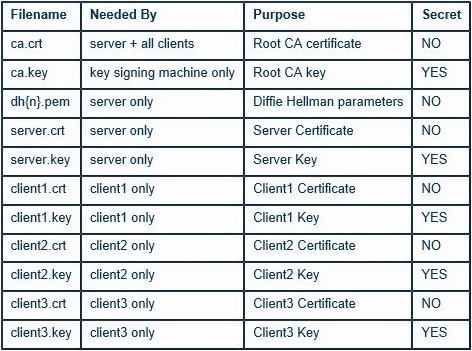
The final step in the key generation process is to copy all files to the machines which need them, taking care to copy secret files over a secure channel.
Execute the su command to get root access.
Execute the following command when you are at my_ca/keys directory: cp ca.crt server.key server.crt dh4096.pem /etc/openvpn/server/ .
Your server.conf file will be placed at Linux here: /etc/openvpn/server.conf. And it will look something like this:
Create the server.conf file at /etc/openvpn/ using this command: cat > server.conf .
Then copy all the configuration above, at the end of the file press “CTRL-C” and the “server.conf” will be created. Create the following directory: mkdir /etc/openvpn/ccd.
Run OpenVPN server like this at /etc/openvpn/: openvpn server.conf
Your OpenVPN server should be running with no errors.
OpenVPN server should be working after booting and running if you used Debian package install. If not or manually installed, you need to get openvpn server.conf at the initscript.
For the client.conf file you need to upload to Hive OS website:
Where ca it’s your “ca.crt” , cert it’s your “client.crt” and key it’s your “client.key” content. You need to copy and paste each of these files content into those 3 fields.
Here at remote dyndns.name.here.org 1994 line, if you have a dynamic IP Address (it’s better if you get some DynDns Service), get a dynamic dns like dyndns.name.here.org, and set it at your local router at DynDns settings so the router update your dynamic IP Address automatically.
Edit the remote directive to point to the hostname/IP address and port number of the OpenVPN server. If your OpenVPN server will be running on a single-NIC machine behind a firewall/NAT-gateway, use the public IP address of the gateway, and a port number which you have configured for the gateway to forward to the OpenVPN server.
To check client’s service status on the rig when you upload config and it’s not working:
OpenVPN
This is how to check the client’s service status on the rig when you upload config and it’s not working:
Just to give you a valid example of the working config: /etc/openvpn/server.conf
And the most important — client.conf. It should go with certificate files.
Please note that in config certificates should be named as in the example:
You can upload files with any names, but then they will be renamed to ca.crt, client.crt, client.key. In this way you will have one config for all rigs.
Also you can embed your certificates into one file to client.conf, so your file will look like this:
Also if you want TLS Auth, you can embed that key in this way:
auth-user-pass is now supported also. So just put this option in client config and upload it with giving login and password in upload dialog.
The Second Tutorial
First of all you need to have a PC or a Server that needs to have a fixed IP on the internal network (the network where you host the VPN Server). Please remember that all VPN traffic will go to the VPN Server machine, coming from each VPN client (each of your rigs and yourself at your personal computer).
We’re assuming you already have installed your VPN Server software at your Windows or Linux. Please note that OpenVPN 2.4 installers will not work on Windows XP.
If you use, for example, Debian, to install OpenVPN just type: apt-get install openvpn . With this you get the Debian OpenVPN package that you will use to set up your OpenVPN server and generate server and client keys.
Links to download OpenVPN and install it manually at the time this tutorial was written:
Configuring
First we need to create the CA certificate. To do this use the following commands:
If you are using Linux, BSD, or a Unix-like OS, open a shell and use the cd command to go to the easy-rsa subdirectory. If you installed OpenVPN from an RPM or DEB file, the easy-rsa subdirectory can usually be found in /usr/share/doc/packages/openvpn or /usr/share/doc/openvpn (it’s best to copy this directory to another location such as /etc/openvpn, before any edits, so that future OpenVPN package upgrades won’t overwrite your modifications). If you installed from a .tar.gz file, the easy-rsa subdirectory will be in the top level directory of the expanded source tree.
At Debian, if you did apt-get install openvpn , execute the following commands:
If you are using Windows, open up a Command Prompt window and use cd to get to \Program Files\OpenVPN\easy-rsa. Run the following batch file to copy configuration files into place (this will overwrite any preexisting vars.bat and openssl.cnf files): init-config .
Now edit the vars file (called vars.bat on Windows / at Linux use the pico vars command) and set the KEY_COUNTRY, KEY_PROVINCE, KEY_CITY, KEY_ORG, and KEY_EMAIL parameters. Don’t leave any of these parameters blank:
Set KEY_SIZE to “4096”
Exit and save the vars file.
At Debian, if you did apt-get install openvpn , run this command: cp openssl-1.0.0.cnf openssl.cnf .
Next, initialize the PKI.
Next, we will generate a certificate and private key for the server.
On Linux/BSD/Unix: ./build-key-server server .
On Windows: build-key-server server .
As in the previous step, most parameters can be defaulted. When the Common Name is queried, enter “server”. Two other queries require positive responses, “Sign the certificate? [y/n]” and “1 out of 1 certificate requests certified, commit? [y/n]”.
Generate certificates & keys for 3 clients. Generating client certificates is very similar to the previous step.
Remember that for each client, make sure to type the appropriate Common Name when prompted, i.e. “client1”, “client2”, or “client3”. Always use a unique common name for each client.
Generate Diffie Hellman parameters
Diffie Hellman parameters must be generated for the OpenVPN server.
On Linux/BSD/Unix: ./build-dh
On Windows: build-dh
Key Files
Now we will find our newly-generated keys and certificates in the keys subdirectory (my_ca/keys). Here is an explanation of the relevant files:
The final step in the key generation process is to copy all files to the machines which need them, taking care to copy secret files over a secure channel.
Execute the su command to get root access.
Execute the following command when you are at my_ca/keys directory: cp ca.crt server.key server.crt dh4096.pem /etc/openvpn/server/ .
Your server.conf file will be placed at Linux here: /etc/openvpn/server.conf. And it will look something like this:
Create the server.conf file at /etc/openvpn/ using this command: cat > server.conf .
Then copy all the configuration above, at the end of the file press “CTRL-C” and the “server.conf” will be created. Create the following directory: mkdir /etc/openvpn/ccd.
Run OpenVPN server like this at /etc/openvpn/: openvpn server.conf
Your OpenVPN server should be running with no errors.
OpenVPN server should be working after booting and running if you used Debian package install. If not or manually installed, you need to get openvpn server.conf at the initscript.
For the client.conf file you need to upload to Hiveon OS website:
Where ca it’s your “ca.crt” , cert it’s your “client.crt” and key it’s your “client.key” content. You need to copy and paste each of these files content into those 3 fields.
Here at remote dyndns.name.here.org 1994 line, if you have a dynamic IP Address (it’s better if you get some DynDns Service), get a dynamic dns like dyndns.name.here.org, and set it at your local router at DynDns settings so the router update your dynamic IP Address automatically.
Edit the remote directive to point to the hostname/IP address and port number of the OpenVPN server. If your OpenVPN server will be running on a single-NIC machine behind a firewall/NAT-gateway, use the public IP address of the gateway, and a port number which you have configured for the gateway to forward to the OpenVPN server.
To check client’s service status on the rig when you upload config and it’s not working:
Hive OS – обзор платформы для майнинга, установка, возможности, цена, плюсы и минусы
 Автор Редакция Profinvestment
 Проверено экспертом Сергей Воробей Обновлено Окт 28, 2022
HiveOS – условно-бесплатная платформа на базе Linux (Ubuntu 16.04 LTS), разработанная специально для добычи криптовалют. Оптимизирована для работы с майнингом на ASIC, GPU. Работает в связке с собственным пулом Hiveon. Система идеальна для майнеров, поскольку предлагает массу полезных функций, начиная от встроенного контроля температуры оборудования и заканчивая интеллектуальными уведомлениями.
Сайт: https://hiveon.com/ru/os (в России может не открываться, используйте VPN или Tor)
Редакция Profinvestment.com рассмотрела более подробно HiveOS и возможности, которые она предоставляет пользователям.
HiveOS
Общая информация
Сколько стоит HiveOS
Операционной системой можно пользоваться бесплатно, но с ограничениями. Кому необходимо, могут оплатить тарифный план и расширить свои возможности. Цены вполне лояльные.
Три доступных тарифа:
- Старт. Цена: бесплатно, если пользоваться пуломHiveOn, в других случаях $3 в месяц. Максимум 4 воркера. Если есть только 1 воркер, он бесплатен независимо от пула. Подробная статистика отображается только за последние три дня. Поддержка возможна путем общения с сообществом (форум, чат).
- Персональный. Цена: GPU — $3 в месяц либо 3 % комиссии пулаHiveon,ASIC – $2 в месяц или бесплатно с пулом Hiveon. Доступен полный спектр функций, 30 дней статистики, техподдержка по email.
- Бизнес. Цена: договорная. Для владельцев 1000+ ригов.
Регистрация на платформе
Перед началом работы следует создать аккаунт. Нажмите « Начать » на главной странице сайта.
Создайте аккаунт, предоставив:
- Действующий адрес электронной почты.
- Логин на свое усмотрение, который еще не занят.
- Пароль высокой сложности, устойчивый к взлому.
На электронный адрес придет письмо активации, нужно перейти по ссылке из него, чтобы завершить создание аккаунта.
Установка HiveOS
После регистрации вы попадете в свой личный кабинет. В настройках можно сменить язык аккаунта на русский.
Нажмите «плюс» на верхней панели, чтобы добавить новую ферму (риг).
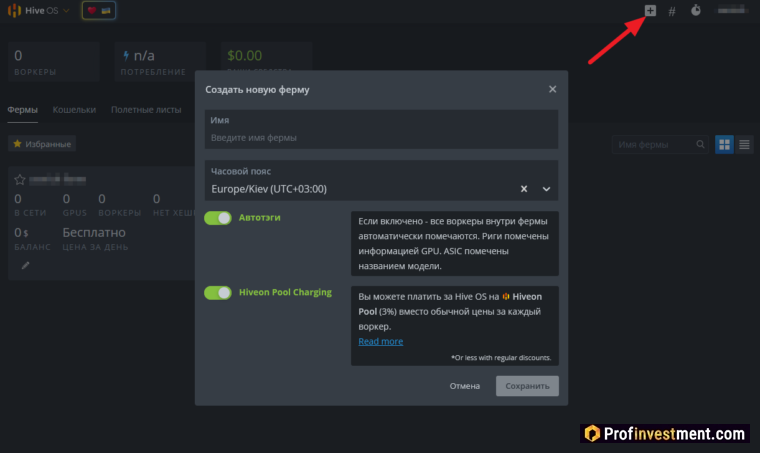
HiveOS — добавление рига
Придумайте имя рига, выберите часовой пояс, в котором работаете.
Обратите внимание на пару настроек:
- Автотеги, если вы хотите, чтобы все единицы вашей фермы автоматически помечались названием модели. Это удобно, например, чтобы быстро определять, с каким из устройств проблемы.
- Pool Charging. По желанию вы можете выбрать, либо оплачивать HiveOS на Hiveon Pool (3 % комиссия пула) или платить фиксированный тариф 3$/месяц за риг в HiveOS. По умолчанию активирована комиссия пула.
Выберите вариант своих устройств – ASIC или GPU. Откроется окно, в котором следует нажать «Установить HiveOS на свой риг». Это самый простой вариант установки.
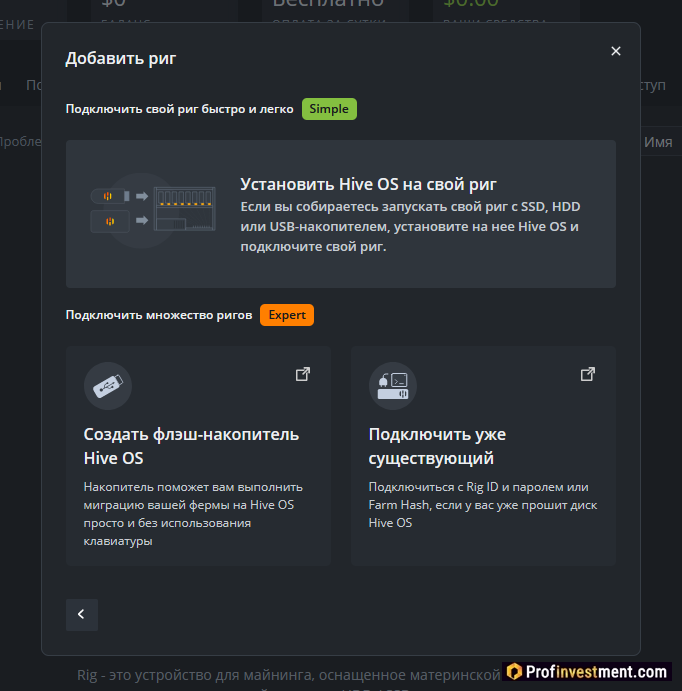
HiveOS — варианты установки
Выберите операционную систему, которой пользуетесь в данный момент – Windows, Linux или MacOS.
Нажмите «Скачать», чтобы загрузить установщик. Запустите скачанный файл. Подготовьте USB-накопитель объемом от 8 Гб, оптимально 16 Гб.
Выберите из раскрывающегося списка версию ОС для загрузки. По умолчанию стоит самая новая. Нажмите Continue.
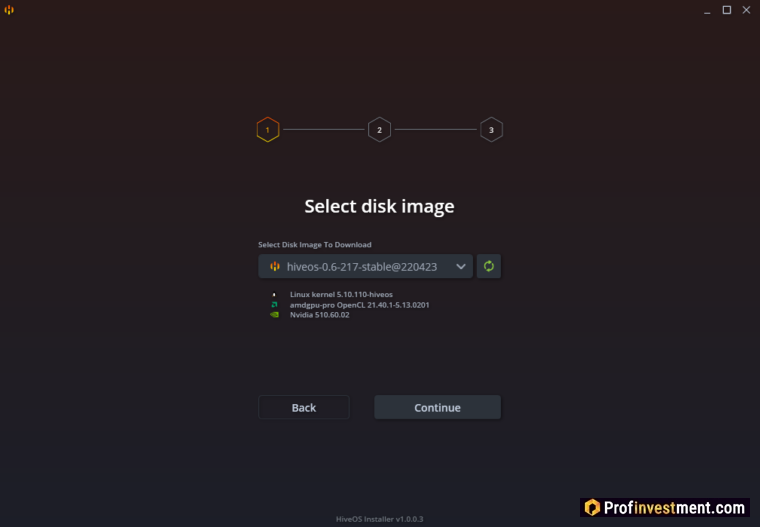
HiveOS — установщик
Введите Farmhash, если поставленный по умолчанию не совпадает. Farmhash – это идентификатор вашей фермы, его можно найти на сайте, если открыть страницу нужной фермы и перейти на вкладку «Настройки», а потом пролистать чуть вниз.
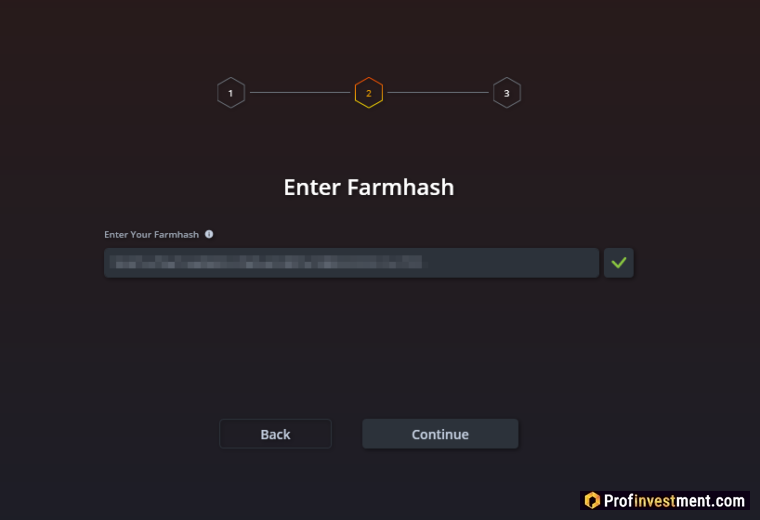
HiveOS — ввод farmhash
На следующем экране выберите USB-накопитель из подключенных к компьютеру и нажмите Flash Image.
Подождите, пока образ операционной системы запишется на флешку. Потом перейдите в корневую папку, найдите файл rig-config-example.txt.
В строке FARM_HASH= введите свой Farmhash, чтобы поле выглядело примерно так:
Нет надобности настраивать RIG_ID и RIG_PASSWD. Сохраните измененный файл и переименуйте его в rig.conf.
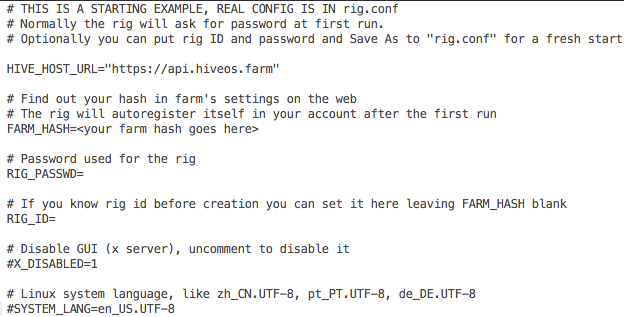
HiveOS — файл конфигурации рига
Наконец, извлеките флешку и вставьте ее в свой риг. Установите систему, и можно начинать работать с Hive.
В настройках ферм можно устанавливать уровни доступа к ним, создавать вотчдоги для удаленного отслеживания температуры и прочих параметров, а также многое другое.
Возможности операционной системы
Пользователям HiveOS доступен целый спектр возможностей для повышения эффективности майнинга. В их числе:
- Мониторинг все процессов в реальном времени и подробная статистика.
- Подключение интеллектуальных уведомлений о событиях и неисправностях в Telegram.
- Удаленное управление через консоль, в том числе и удаленное обновление ОС, перезагрузка/выключение.
- Контроль температуры оборудования. Умное охлаждение (autofan). Автоматически управляет работой вентиляторов, чтобы температура оборудования была на приемлемом уровне.
- Поддержка большого количество майнеров.
- Поддержка
- Настройка расписания. Функция позволяет автоматизировать определенные процессы. Например, настроить воркеров на переключение с разгона на понижающее напряжение; действие будет выполняться автоматически, даже без вашего участия.
- Оптимизация энергопотребления.
- Быстрое переключение пула и майнеров при необходимости.
- Индивидуальные настройки для каждого майнера.
- Интегрированные возможности для разгона видеокарт.
- API.
- Вотчдоги.
- ASIC-хаб и прошивки для ASIC.
Статистика – одно из самых ценных преимуществ HiveOS, потому что позволяет отслеживать производительность каждого из воркеров при различных температурах, скоростях вращения вентиляторов, алгоритмах и пр. Благодаря этой информации, вы можете понять, как работают устройства при разных параметрах, и определить, какие комбинации являются наиболее эффективны. Тем самым – увеличить прибыль.
Как обезопасить аккаунт
Нажав на имя пользователя в верхнем углу справа на странице обзора ферм, выберите пункт «Аккаунт», просмотрите вкладки на открывшейся странице.
Важно защитить учетную запись от взлома при помощи 2FA (двухфакторной аутентификации). Для этой цели можно установить на телефон приложение Google Authenticator, затем включить 2FA в настройках, следуя инструкциям.
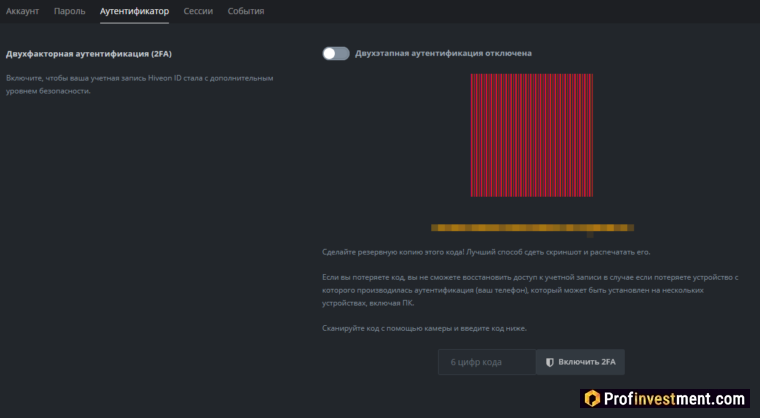
HiveOS — подключение 2FA
Если вы потеряли телефон и нужно сбросить 2FA, обратитесь в техподдержку, указав данные от своего аккаунта HiveOS, количество и названия воркеров, адрес основного криптокошелька, а также IP последнего входа в аккаунт и примерное время.
Для защиты аккаунта не помешает также отслеживать токены, которые появляются в разделе «Токены аутентификации» и удалять те, которые вам не известны. То же касается удаления неизвестных лиц из списка доступа к ферме.
HiveOS можно обновлять двумя способами:
- Автоматически.
- Принудительно.
Во втором случае репозитории полностью очищаются, обновляются и устанавливаются повторно. Если вам понадобится понизить версию системы, то для этого на панели инструментов есть специальная стрелочка и выбор версии.
Hiveon Pool
Пользователям HiveOS удобнее и выгоднее всего майнить на Hiveon Pool. Впрочем, пул доступен и для тех, кто не пользуется системой.