Remove Ocsp.comodoca.com Pop-up Ads
Can’t Remove Ocsp.comodoca.com ads ? This page includes detailed ads by Ocsp.comodoca.com Removal instructions!
Do you get redirected to ocsp.comodoca.com and other bizarre websites? Are you unable to find what you search for online? Do you come across pop-up ads on a daily basis? Is your computer sluggish? You’re dealing with a parasite. The silver lining here is that this program is relatively easy to tackle. What you’re stuck with is a potentially unwanted adware infection. Those are more annoying than they are dangerous. However, don’t underestimate the intruder. The more time it spends on board, the more problematic it becomes. Are you willing to risk it? Your situation could become a lot worse if you hesitate for too long. Take action on the spot. You won’t regret it. On the other hand, you will regret keeping the virus on board. No cyber infection belongs on your machine. After all, malware gets developed to serve hackers’ malicious purposes. The adware starts messing with you immediately after installation. It adds an extension to your browsers. Thanks to this pesky plugin, the parasite takes control over your overall online experience. You’re about to witness numerous changes in your default browsing settings. It goes without saying all of them are completely unauthorized. Crooks don’t need to take your opinions into consideration. They inject your browsers with pop-ups for one very simple reason. The ocsp.comodoca.com pop-up ads are sponsored. By displaying them, crooks gain profit. Easy, illegitimate revenue is every single crook’s dream. That explains why the commercials are impossible to get rid of. Furthermore, a sponsored ad is never a reliable one. There are some corrupted ads on your PC screen so watch out for malware. If you click the wrong pop-up, you’ll automatically download more infections. Yes’ it’s that simple. Adware can’t cause you harm directly. It lets you do the job instead. To protect your PC, avoid the pesky ocsp.comodoca.com pop-up ads. These stubborn web links cover all websites you visit. Or, should we say, attempt to visit. Surfing the Web with an adware-type virus on board is, to say the least, difficult. Pop-ups, pop-unders, banners, interstitials, video ads, etc. In this mess of commercials, you must do the right thing. Restrain yourself from clicking the ads and delete the virus instead. This infection also puts in danger your private information. It collects browsing-related data such as passwords, usernames, browsing history. The parasite might get to some personally identifiable information as well. To prevent financial scams and identity theft, tackle the virus now.
How did I get infected with?
The easiest explanation is a freeware or shareware bundle. Many people use those to download a bunch of programs at once. However, many hackers use them too. Stay away from illegitimate program packages and websites. Check out what you’re about to download as well. Unless you make a thorough check, you might compromise your PC yourself. Never overlook a potential threat online. It is easier to prevent installation than to remove a virus after that. Save yourself the trouble. Take your time in the process. Skipping steps may leave your device open to parasites. In addition, go through the EULA or Terms and Conditions. You must be aware what you give green light to, right? Another tactic involves spam email-attachments. If you stumble across some random email from an unknown sender, delete it. Chances are, it’s immensely dangerous. The same piece of advice goes for your messages in social media. Be cautious and always make sure you outwit hackers.
Why is this dangerous?
The ocsp.comodoca.com pop-up ads are, without a doubt, malicious. These obnoxious links will lead you to unsafe websites. Before you know it, they might bring along further damage. As we mentioned already, the adware adds a plugin to your browsers. It’s compatible with Google Chrome, Mozilla Firefox and Internet Explorer. You don’t have a single reliable browser right now. Therefore, you’re forced to deal with the pop-ups all the time. This infection also redirects you to unknown pages that might turn out to be harmful. It causes your browsers to frequently crash. Even your Internet connection might become unstable all of a sudden. Last but not least, your privacy is now jeopardized. To delete the virus manually (which is a must), please follow our detailed removal guide. You’ll find it down below.
How to Remove Ocsp.comodoca.com virus
Please, have in mind that SpyHunter offers a free 7-day Trial version with full functionality. Credit card is required, no charge upfront.
The Ocsp.comodoca.com infection is specifically designed to make money to its creators one way or another. The specialists from various antivirus companies like Bitdefender, Kaspersky, Norton, Avast, ESET, etc. advise that there is no harmless virus.
If you perform exactly the steps below you should be able to remove the Ocsp.comodoca.com infection. Please, follow the procedures in the exact order. Please, consider to print this guide or have another computer at your disposal. You will NOT need any USB sticks or CDs.
Please, keep in mind that SpyHunter’s scanner tool is free. To remove the Ocsp.comodoca.com infection, you need to purchase its full version.
STEP 1: Track down Ocsp.comodoca.com in the computer memory
- Open your Task Manager by pressing CTRL+SHIFT+ESC keys simultaneously
- Carefully review all processes and stop the suspicious ones.
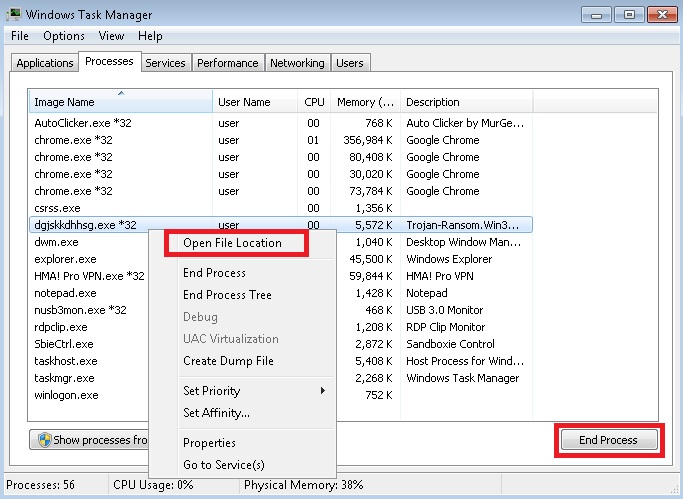
- Write down the file location for later reference.
Step 2: Locate Ocsp.comodoca.com startup location
Reveal Hidden Files
- Open any folder
- Click on “Organize” button
- Choose “Folder and Search Options”
- Select the “View” tab
- Select “Show hidden files and folders” option
- Uncheck “Hide protected operating system files”
- Click “Apply” and “OK” button
Clean Ocsp.comodoca.com virus from the windows registry
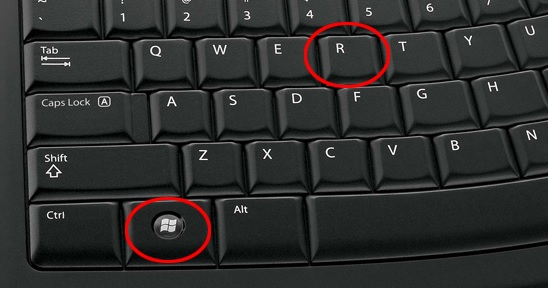
- Once the operating system loads press simultaneously the Windows Logo Button and the R key.
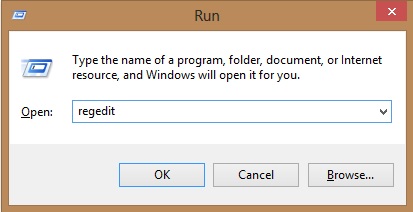
- A dialog box should open. Type “Regedit”
- WARNING! be very careful when editing the Microsoft Windows Registry as this may render the system broken.
Depending on your OS (x86 or x64) navigate to:
[HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run] or
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] or
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run]
- and delete the display Name: [RANDOM]
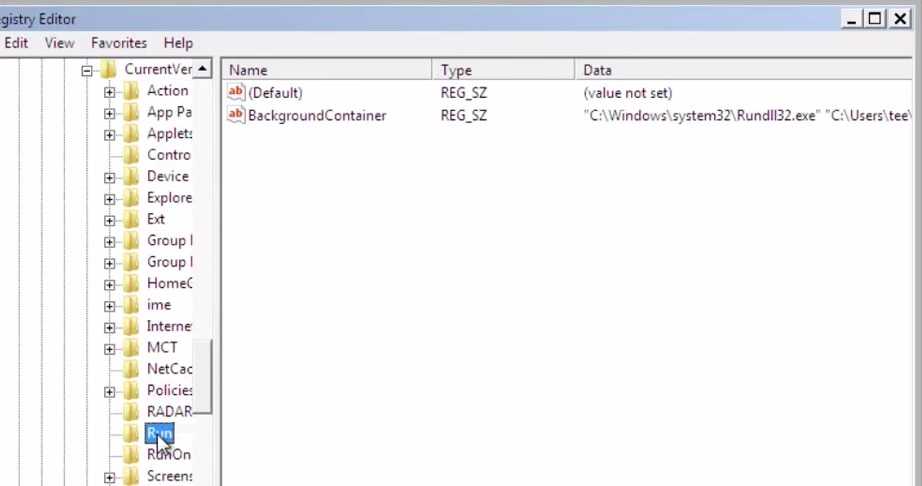
- Then open your explorer and navigate to: %appdata% folder and delete the malicious executable.
Clean your HOSTS file to avoid unwanted browser redirection
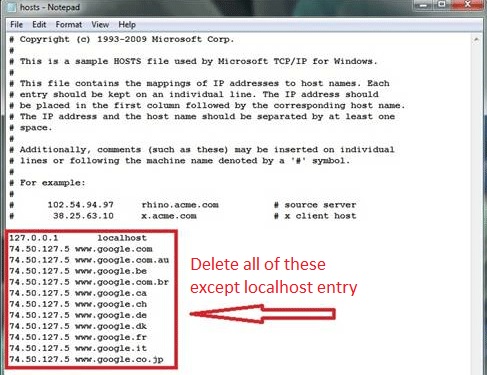
Navigate to %windir%/system32/Drivers/etc/host
If you are hacked, there will be foreign IPs addresses connected to you at the bottom. Take a look below:
STEP 3 : Clean Ocsp.comodoca.com traces from Chrome, Firefox and Internet Explorer
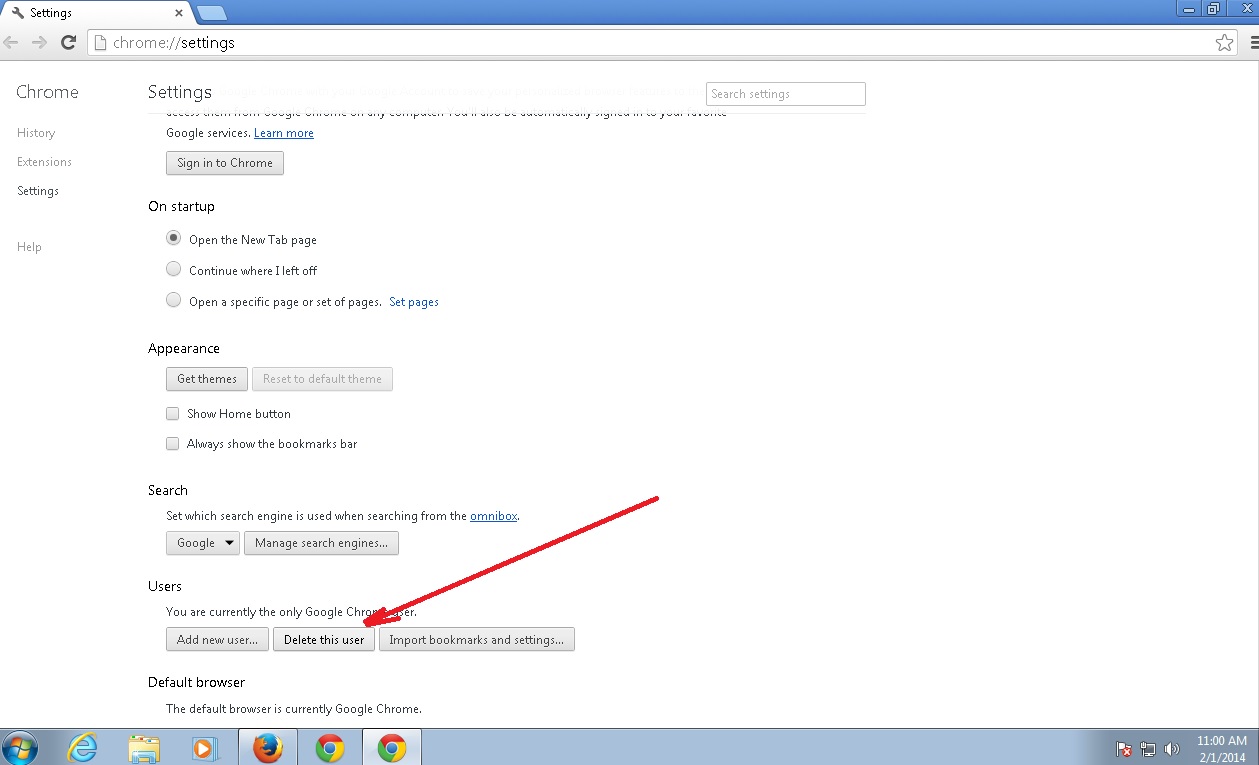
Open Google Chrome
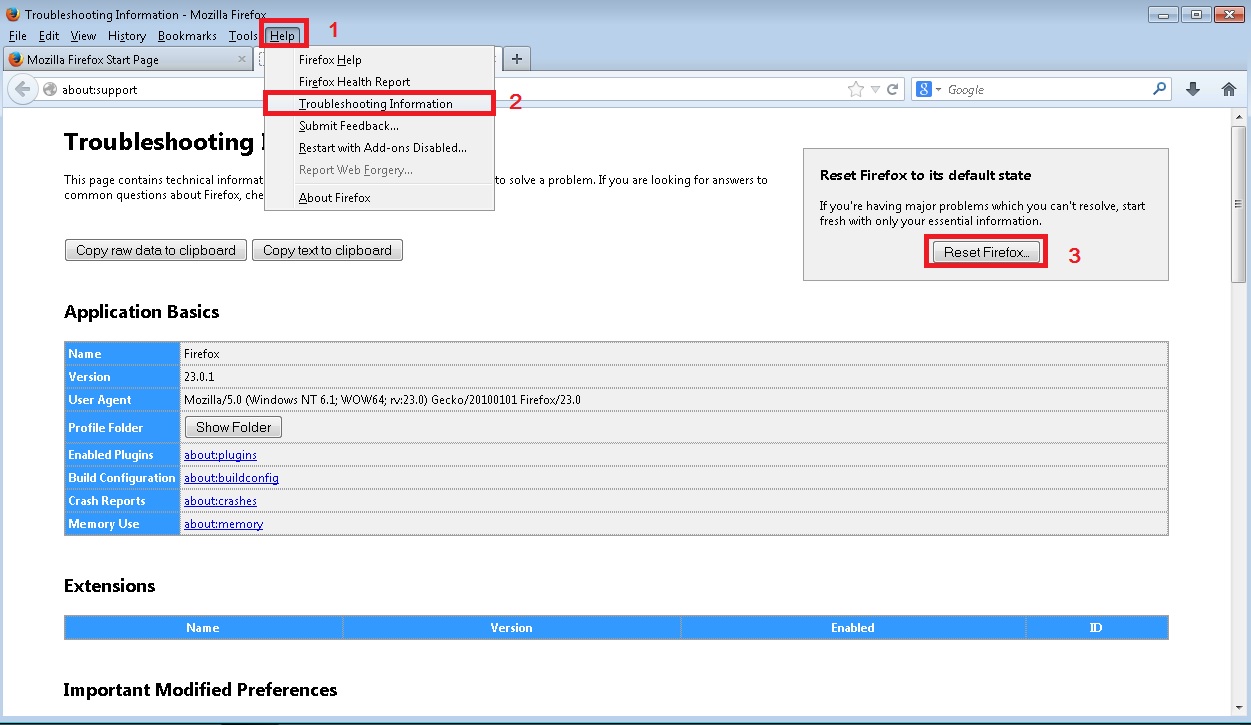
Open Mozilla Firefox
Open Internet Explorer
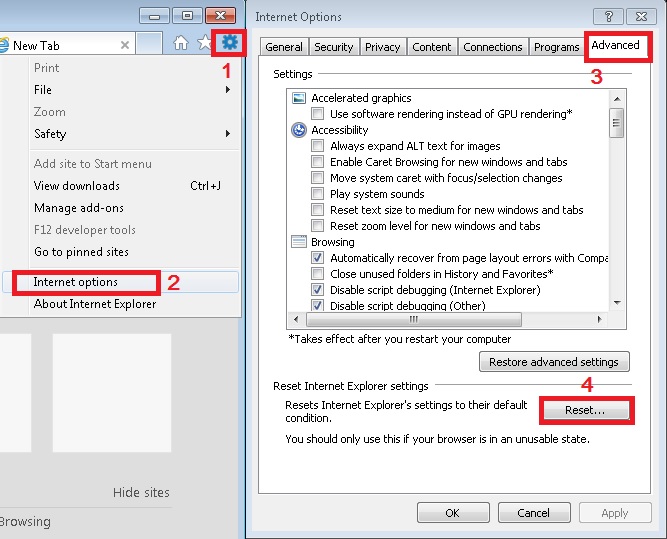
- Restart Internet Explorer
Step 4: Undo the damage done by Ocsp.comodoca.com
This particular Virus may alter your DNS settings.
Attention! this can break your internet connection. Before you change your DNS settings to use Google Public DNS for Ocsp.comodoca.com, be sure to write down the current server addresses on a piece of paper.
To fix the damage done by the virus you need to do the following.
- Click the Windows Start button to open the Start Menu, type control panel in the search box and select Control Panel in the results displayed above.
- go to Network and Internet
- then Network and Sharing Center
- then Change Adapter Settings
- Right-click on your active internet connection and click properties. Under the Networking tab, find Internet Protocol Version 4 (TCP/IPv4). Left click on it and then click on properties. Both options should be automatic! By default it should be set to “Obtain an IP address automatically” and the second one to “Obtain DNS server address automatically!” If they are not just change them, however if you are part of a domain network you should contact your Domain Administrator to set these settings, otherwise the internet connection will break.
You must clean all your browser shortcuts as well. To do that you need to
- Right click on the shortcut of your favorite browser and then select properties.
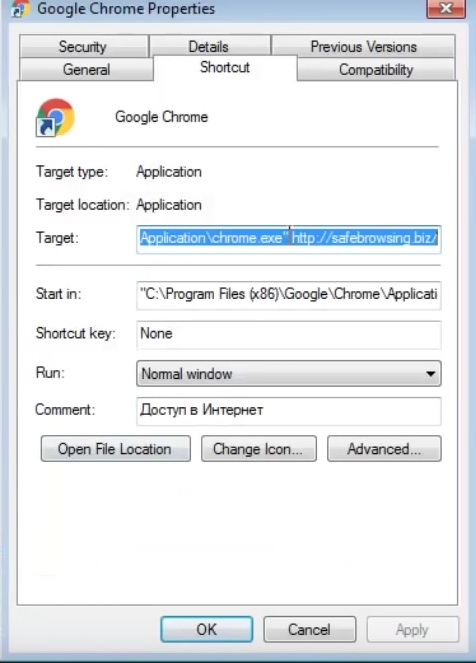
- in the target field remove Ocsp.comodoca.com argument and then apply the changes.
- Repeat that with the shortcuts of your other browsers.
- Check your scheduled tasks to make sure the virus will not download itself again.
How to Permanently Remove Ocsp.comodoca.com Virus (automatic) Removal Guide
Please, have in mind that once you are infected with a single virus, it compromises your system and let all doors wide open for many other infections. To make sure manual removal is successful, we recommend to use a free scanner of any professional antimalware program to identify possible registry leftovers or temporary files.
Remove ocsp.comodoca.com
If you notice your computer being often directed towards ocsp.comodoca.com you might be infected with an adware.
This url address (ocsp.comodoca.com) belongs to Comodo, and it’s usually used to verify certificates under the OCSP protocol. What might be happening here is that an unwanted program is blocking this protocol, therefore the validation system attempts to verify certificates through ocsp.comodoca.com.
We are more than certain that there’s an unwanted program behind this problem. Most likely we’re dealing here with an adware you downloaded and installed yourself, although not on purpose, while installing some free tool. In fact it’s quite common to find this kind of unwanted program attached to fake tools and updates (fake codecs, fake video players) often found in streaming websites. What they’re are trying to achieve is to be installed as quietly as possible so they can fill you with ads afterwards.
It’s not easy to remove this kind of unwanted programs, specially if you attempt to do it manually. To be successful in stopping all those sudden accesses to ocsp.comodoca.com you should use a free tool that will completely scan your system to find and remove all unwanted programs already running on it. You’ll find in our guide below the best free tools to achieve this goal.
How to remove ocsp.comodoca.com ?
Step 1 — Remove ocsp.comodoca.com with Malwarebytes Anti-Malware
Step 2 — Remove ocsp.comodoca.com using Adwcleaner
Step 3 — Remove ocsp.comodoca.com with ZHPCleaner
Step 4 — Remove ocsp.comodoca.com with Junkware Removal Tool
Step 5 — Remove ocsp.comodoca.com with HitmanPro
Remove ocsp.comodoca.com with MalwareBytes Anti-Malware
Malwarebytes Anti-Malware is a light-weight anti-malware program that is excellent at removing the latest detections.
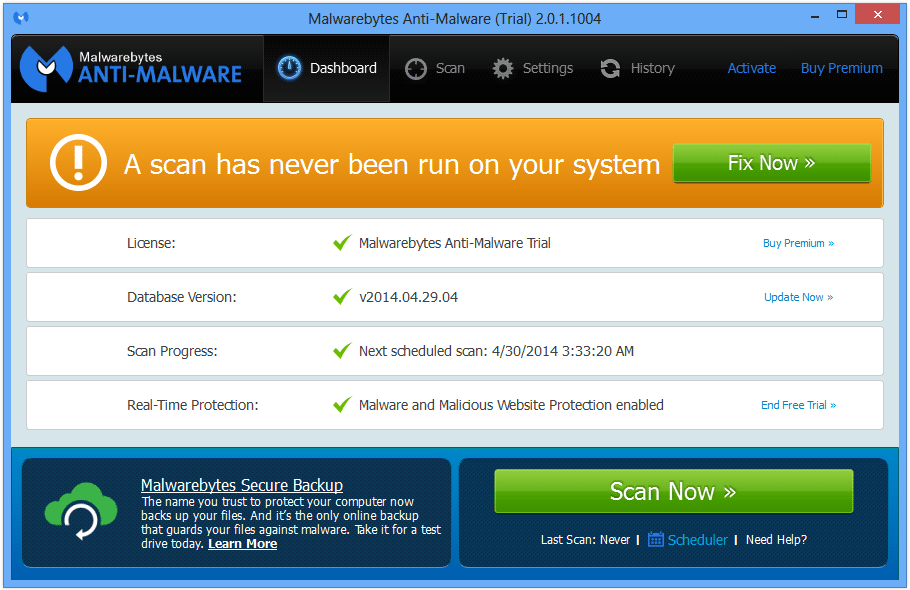
- Download Malwarebytes Anti-Malware to your desktop.
Premium VersionFree Version (without Real-time protection) - Install MalwareBytes Anti-Malware using the installation wizard.
- Once installed, Malwarebytes Anti-Malware will automatically start and you will see a message stating that you should update the program, and that a scan has never been run on your system. To start a system scan you can click on the Fix Now button.
- If an update is found, you will be prompted to download and install the latest version.
- Malwarebytes Anti-Malware will now start scanning your computer for ocsp.comodoca.com.
- When the scan is complete, make sure that everything is set to Quarantine, and click Apply Actions.
- When removing the files, Malwarebytes Anti-Malware may require a reboot in order to remove some of them. If it displays a message stating that it needs to reboot your computer, please allow it to do so.
Remove ocsp.comodoca.com with AdwCleaner
AdwCleaner is a helpful tool developed to remove undesired toolbars, browser hijackers, redirects and potentially unwanted programs (PUPs) in Internet Explorer, Firefox, Chrome or Opera. AdwCleaner requires no installation and can be ran in a instantaneous to examine your computer.
- Please download AdwCleaner by Xplode and save to your Desktop :
Download AdwCleaner - Double-click on AdwCleaner.exe to run the tool (Windows Vista/7/8 users : right-click and select Run As Administrator).
- Click on the Scan button.
- After the scan has finished, click on the Clean button..
- Press OK again to allow AdwCleaner to restart the computer and complete the removal process.
Remove ocsp.comodoca.com with ZHPCleaner
ZHPCleaner is a program that searches for and deletes Adware, Toolbars, Potentially Unwanted Programs (PUP), and browser Hijackers from your computer. By using ZHPCleaner you can easily remove many of these types of programs for a better user experience on your computer and while browsing the web.
- If Avast is installed on you computer you have to disable it during the process.
- You can download AdwCleaner utility from the below button :
Download ZHPCleaner - Select ZHPCleaner.exe with right mouse click and Run as Administrator.
- Accept the user agreement.
- Click on the Scanner button.
- After the scan has finished, click on the Repair button.
- Reboot your computer.
Remove ocsp.comodoca.com with Junkware Removal Tool
Junkware Removal Tool is a security utility that searches for and removes common adware, toolbars, and potentially unwanted programs (PUPs) from your computer. A common tactics among freeware publishers is to offer their products for free, but bundle them with PUPs in order to earn revenue. This tool will help you remove these types of programs.
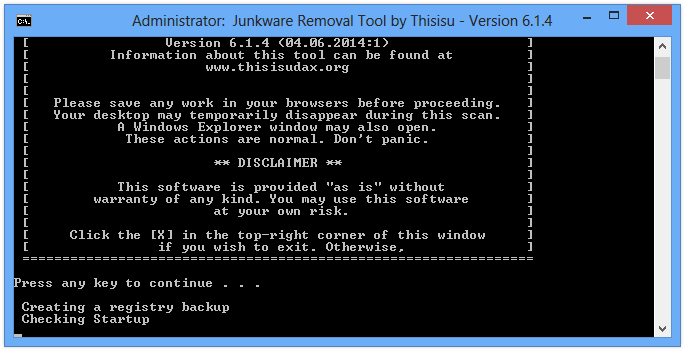
- Download Junkware Removal Tool (Official link and direct-download) :
Download Junkware Removal Tool - Select JRT.exe with right mouse click and Run as Administrator
- If User Account Control asks you to allow JRT.exe to make changes to your computer, press Yes to continue..
- Close all your browsers, save any work and then press any key to continue.
- When Junkware Removal Tool is done scanning and removing malicious items from your computer a logfile will open.
Remove ocsp.comodoca.com with HitmanPro
HitmanPro is an anti-virus program that describes itself as a second opinion scanner that should be used in conjunction with another anti-virus program that you may already have installed.
Comodo OCSP
After I started the gVim text editor on a Windows laptop, I saw a «firewall alert» from the Symantec antivirus/firewall software on the system stating «Suspicious network activity has been detected.» I’ve used gVim on many other systems for many years, but those systems weren’t running the Symantec security software. The Symantec software showed that gvim.exe was attempting a Domain Name System (DNS) query to port 53, the well-known port for DNS, to IP address 8.8.8.8, the Google DNS server specified on the system for DNS queries.
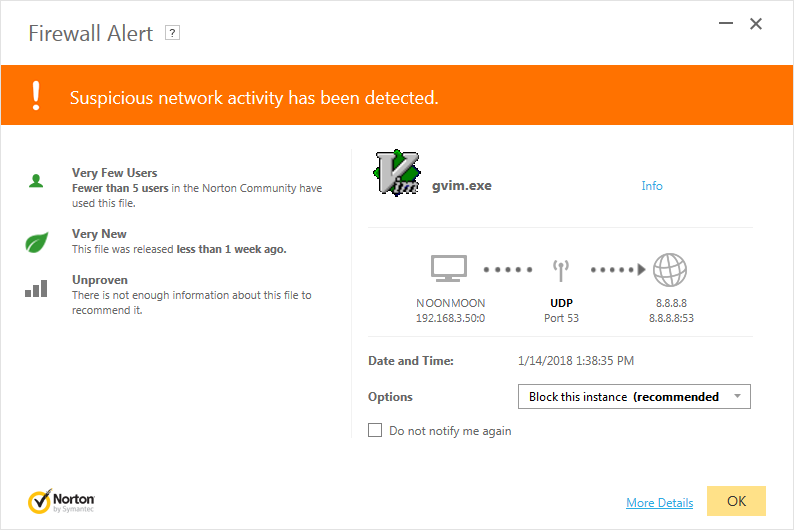
Since I was curious as to the details for the DNS query the gVim editor program wanted to submit, I blocked the query until I started the Wireshark packet analyzer program I already had installed on the laptop to capture the network traffic. I then allowed the DNS query and filtered the Wireshark data with a tcp.port == 53 || udp.port == 53 filter to see just the DNS traffic and saw a DNS query to 8.8.8.8 to look up the IP address for ocsp.trust-provider.com, a domain registered to CSC Corporate Domains in Wilmington DE in the U.S. The address returned for the fully qualified domain name (FQDN) was 178.255.83.1. The DNS answer from the Google name server is shown below:
The ocsp.trust-provider.com FQDN is an alias for ocsp.comodoca.com , thus the CNAME reference. I removed the Wireshark filter to see the subsequent non-DNS traffic and saw a a Hypertext Transfer Protocol (HTTP) connection to 178.255.83.1 on port 80. The requested Uniform Resource Identifier (UR) was as follows:
[Full request URI: http://ocsp.trust-provider.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBR8sWZUnKvbRO5iJhat9GV793rVlAQUrb2YejS0Jvf6xCZU7wO94CTLVBoCEENSAj%2F6qJAfE5%2Fj9OXBRE4%3D]
OCSP stands for «Online Certificate Status Protocol», which is an Internet protocol used to check the validity of security certificates for websites and is described in RFC 6960, X.509 Internet Public Key Infrastructure Online Certificate Status Protocol — OCSP. Wireshark showed the following OCSP response:
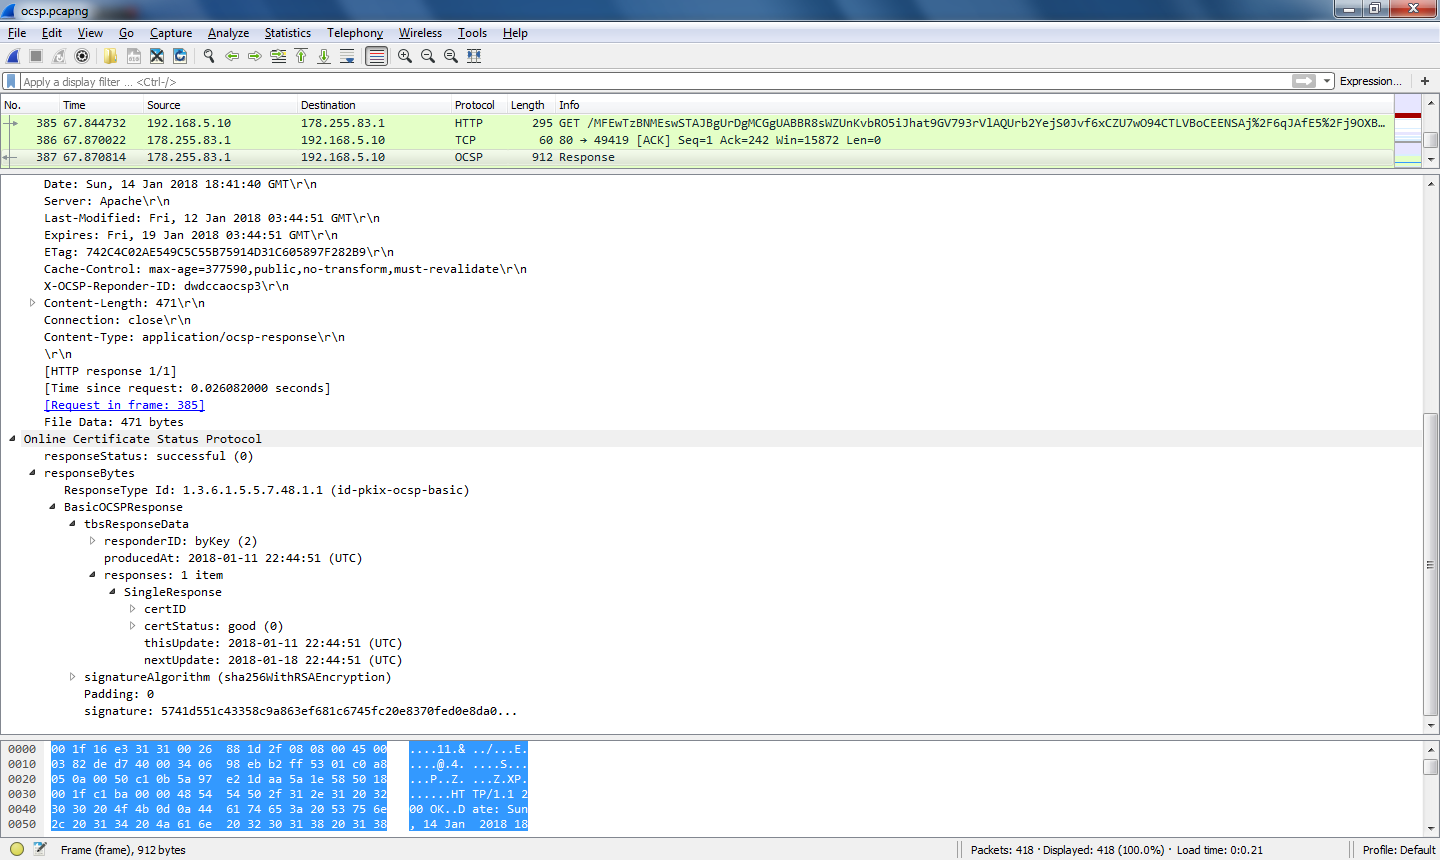
When I looked at the details of the OCSP response, I saw «responseStatus: successful (0)» and «certStatus: good (0)». I also saw the following values:
producedAt: 2018-01-11 22:44:51 (UTC)
thisUpdate: 2018-01-11 22:44:51 (UTC)
nextUpdate: 2018-01-18 22:44:51 (UTC)
The timestamps were in Coordinated Universal Time (UTC); UTC, aka GMT and zulu time, is currently 5 hours ahead of the time zone I’m in. The three values have the following meaning according to the RFC:
So the status provided by the OCSP server was last updated about 3 days ago and will next be updated in about 4 more days.
After the HTTP exchange between the laptop and OCSP server, I saw another DNS query from the laptop, but this time for ocsp.comodoca4.com . The same IP address was returned, 178.255.83.1.
The URI requested was as follows:
[Full request URI: http://ocsp.comodoca4.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrJdiQ%2Ficg9B19asFe73bPYs%2BreAQUdXGnGUgZvJ2d6kFH35TESHeZ03kCEFslzmkHxCZVZtM5DJmpVK0%3D]
The response from the OCSP server seemed similar to the one before with the same producedAt, thisUpdate, and nextUpdate values. I decoded both OCSP queries using the decode-ocsp-get Python script written by Malini Kothapalli and also available for download here. The usage information for the script is shown below:
When I used the -r option to query the two URLs I had seen in the Wireshark data capture, I saw the following:
I downloaded the .crt file, which is an X.509 certificate encoded as binary DER or ASCII PEM, from http://crt.comodoca.com/COMODOECCCertificationAuthority.crt to the Windows 7 laptop and then double-clicked on it to open it. The certificate was issued to «COMODO ECC Certification Authority.
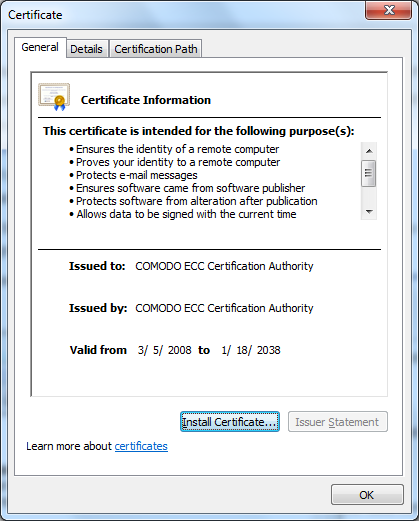
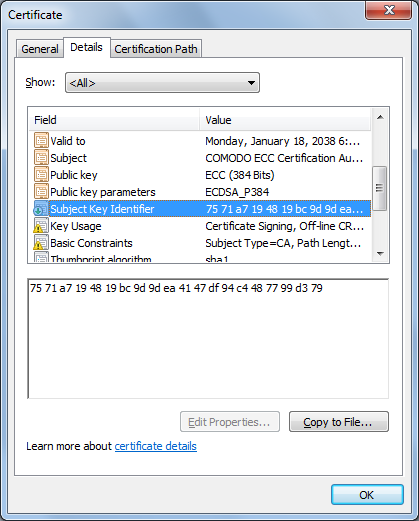
When I clicked on the Details tab and looked at the «Subject Key Identifier» field, I saw it matched the Issuer Key Hash for the result from ./decode-ocsp-get.py -r http://ocsp.comodoca4.com/MFEwTzBNMEswSTAJBgUrDgMCGgUA .
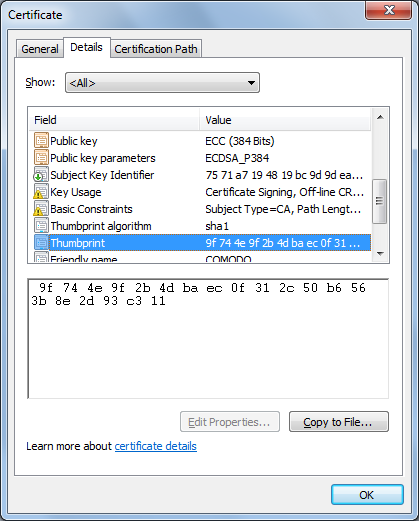
The thumbprint value, 9F744E9F2B4DBAEC0F312C50B6563B8E2D93C311, matched the SHA1 Fingerprint value, I saw at the Mozilla Foundation’s Add COMODO ECC Certification Authority root certificate and enable it for EV page. The Mozilla Foundation supports the development of the Firefox web browser.
I uploaded the COMODOECCCertificationAuthority.crt file to a Linux system and then converted the .crt file to a .pem file using the openssl utility. You can convert Convert a DER file (.crt .cer .der) to PEM using a command in the form openssl x509 -inform der -in certificate.cer -out certificate.pem .
You can filter on just OCSP traffic in Wireshark using a filter of ocsp . When I applied that filter, I found that there was a prior OCSP packet before the ones I had been examining going to IP address 104.25.219.21 that showed references to certificates for the following systems:
OCSP stapling в Nginx
В зависимосте от типа сертификата в архиве могут быть другие файлы:
В этом случае команда выглядит так
Да, так советует делать инструкция от Comodo. Но в таком случае на SSLLabs будет предупреждение Chain issues — Contains anchor. Поэтому AddTrustExternalCARoot.crt нужно исключить �� и правильная команда выглядит так
Далее нам нужен файл, содержащий сертификаты (корневой+промежуточный) для проверки ответов OCSP
Если нужно скачать сертификаты ��♂️
Пример конфигурационного файла для OCSP stapling
Слишком маленькое значение resolver_timeout (менее 5 секунд) может вызвать ошибку ��
Если настроен фаервол, то не забудьте разрешить вашему серверу исходящие соединения к OCSP URL .
Раз уж теперь известен OCSP сервер, то можно провести тест через консоль с openssl.
Успешный вывод команды выглядит так
Если вдруг Responder Error: unauthorized, то читаем RFC5019