Saved searches
Use saved searches to filter your results more quickly
You signed in with another tab or window. Reload to refresh your session. You signed out in another tab or window. Reload to refresh your session. You switched accounts on another tab or window. Reload to refresh your session.
m1stadev / Inferius Public archive
Create & Restore 64-bit custom IPSWs
License
m1stadev/Inferius
Name already in use
- Local
- Codespaces
Use Git or checkout with SVN using the web URL.
Work fast with our official CLI. Learn more about the CLI.
Sign In Required
Please sign in to use Codespaces.
Launching GitHub Desktop
If nothing happens, download GitHub Desktop and try again.
Launching GitHub Desktop
If nothing happens, download GitHub Desktop and try again.
Launching Xcode
If nothing happens, download Xcode and try again.
Launching Visual Studio Code
Your codespace will open once ready.
There was a problem preparing your codespace, please try again.
Latest commit
Git stats
Files
Failed to load latest commit information.
README.md
Inferius is an xpwn-like tool to create & restore custom IPSWs to 64-bit devices.
Its current purpose is to downgrade devices (vulnerable to checkm8) to previous iOS versions. However, there are other possible uses for this tool as well.
Notes and Caveats
Before using Inferius, keep in mind that
- No one but YOU is fully responsible for any data loss or damage caused to your device
- Downgrades are currently limited to versions compatible with the latest signed SEP version.
- Due to the downgrades being tethered, after restoring a custom IPSW you must patch the bootchain & send it to your device over pwned DFU manually to boot, as described here, or use one of these tools to automate the process for you:
By default, firmware bundles are automatically downloaded from an external repo. However, if there isn’t a firmware bundle for the device+iOS version combo you’re attempting to downgrade to, you’ll need to create your own using bundlegen.
Pull requests for new firmware bundles are welcome, as long as the firmware bundle you want to add can create a usable IPSW for the targeted version.
| Option (short) | Option (long) | Description |
|---|---|---|
| -d IDENTIFIER | —device IDENTIFIER | Device identifier |
| -f IPSW | —ipsw IPSW | Path to IPSW |
| -c | —create | Create custom IPSW |
| -r | —restore | Restore custom IPSW |
| -b | —bundle BUNDLE | (Optional) Path to local Firmware Bundle |
| -u | —update | Keep data while restoring custom IPSW |
- A computer running macOS or Linux
- At least 10gbs of free space on your computer
- An Internet connection
- A 64-bit device (vulnerable to checkm8)
- A firmware bundle for your device & the iOS version to be downgraded to
- If there isn’t a firmware bundle for your device + iOS version combo, look at bundlegen
- futurerestore must be compiled with my fork of img4tool, or else it can’t be used with Inferius.
- pip3 install -r requirements.txt
- Implement iOS 10 downgrades for A7 devices.
- Update bundle documentation
Inferius Bundle Generator
Option (short) Option (long) Description -d IDENTIFIER —device IDENTIFIER Device identifier -i VERSION —version VERSION iOS version - A computer running macOS
- At least 250mbs of free space on your computer
- An Internet connection
- A compiled binary can be found here
- A compiled binary can be found here
- A compiled binary can be found here
- A compiled binary can be found here
- pip3 install -r requirements.txt
-
for asr64_patcher for creating many Firmware Bundles and beta testing , Chibibowa, and Moses for beta testing
Finally, if you need help or have any questions about Inferius, join my Discord server.
Inferius – Create and Restore Custom IPSWs on 64-bit devices
Custom firmware are back from the dead, but this time they work on 64-bit devices! Written from the ground up in Python, Inferius is a new utility that lets you create custom firmware for 64-bit devices. Here’s all you need to know about it.
Table of Contents
What is Inferius?
Inferius is an xpwn-style tool that can create custom IPSW files and restore 64-bit devices. It is developed by marijuanaARM.
In layman’s terms, it is a downgrade utility that lets you easily downgrade to older iOS versions. You can also downgrade without SHSH Blobs with Inferius.
However, it will be a tethered downgrade, meaning you will need a computer to boot your device up.
It’s worth noting that Inferius does not come with all firmware bundles out of the box. If it lacks the required firmware bundle, you can create one of your own by following this guide.
You can also request the developer to add the necessary firmware bundles on his private Discord server.
Before you start creating your custom IPSW files, there are a few limitations you must know about.
- Firstly, you are limited to versions compatible with the current SEP firmware version. For instance, if you are running iOS 13.6.1, the lowest version you could possibly downgrade to will be iOS 13.4.
- Secondly, you must boot your device manually with a computer (tethered boot) using ra1nsn0w or PyBoot utility if you perform a custom IPSW restore.
- Finally, you must use a checkm8-compatible device. Inferius does not support devices with the A12 and A13 system-on-chips. You can get the full list of compatible devices here.
Warning – We strongly recommend creating a fresh custom IPSW firmware if you want to restore your device. Older custom IPSW might brick your device as Inferius needs to fetch the LLB and iBoot from a signed firmware version.
Download Inferius
Requirements
- A computer running macOS
- A 64-bit Apple device vulnerable to checkm8
- ldid
How to create custom IPSW firmware using Inferius
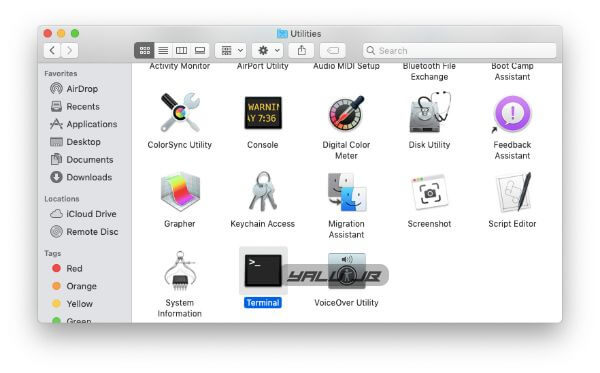
Step 1 First and foremost, fire up the Terminal. Go to Applications > Utilities and launch Terminal.
Step 2 Install brew package manager on your Mac. Skip this step if brew is already installed on your computer.
Inferius как работает downgrade
Reddit and its partners use cookies and similar technologies to provide you with a better experience.
By accepting all cookies, you agree to our use of cookies to deliver and maintain our services and site, improve the quality of Reddit, personalize Reddit content and advertising, and measure the effectiveness of advertising.
By rejecting non-essential cookies, Reddit may still use certain cookies to ensure the proper functionality of our platform.
For more information, please see our Cookie Notice and our Privacy Policy .
Get the Reddit app
We stand in solidarity with numerous people who need access to the API including bot developers, people with accessibility needs (r/blind) and 3rd party app users (Apollo, Sync, etc.) If you need jailbreak help, join our Discord at https://discord.gg/jb.
hello . i have problem. I can't figure out how to compile futurerestore and img4tool correctly. I also found a compiled futurerestore specifically for inferius, but I don’t know in which folder to insert it. Mac OS Catalina
Jailbreak iOS 13.6 and iOS 13.6.1
We have discussed everything you need to know about iOS 13.6 and iOS 13.6.1 jailbreak information on this page. Also you can find iOS 13, iOS 13.1, iOS 13.1.1, iOS 13.1.2, iOS 13.1.3, iOS 13.2, iOS 13.2.2, iOS 13.2.3, iOS 13.3, iOS 13.3.1, iOS 13.4, iOS 13.4.1, iOS 13.5, iOS 13.5.1 jailbreak methods.
Please refer to the following pages if you have already upgraded to iOS 13.7 or iOS 14 – iOS 14.8.1, iOS 15 – iOS 15.7.7, iOS 16 – iOS 16.6 and iOS 17 beta.
1) Hexxa Plus (Version 5.49)
Hexxa plus Version 5.49 has been released as the iOS 13.6 / iOS 13.6.1 Jailbreak solution. It is compatible with all iOS 13 and higher versions including iOS 13.5, iOS 13.5.1,iOS 13.6 and iOS 13.6.1. Hexxa Plus is an Online Jailbreak solution that works with all the latest iPhone and iPad models including iPhone 11, 11 Pro, Pro Max, iPhone XS, XS Max, XR etc.
2) Odyssey Jailbreak (Version 1.3)
Odyssey is an IPA based semi-untethered jailbreak tool for all iOS 13 versions. You can install it using Altstore (computer) or using Wander (Online). Odyssey Jailbreak is compatible with iOS 13.5.1, iOS 13.6 & iOS 13.6.1 now.
3) Unc0ver Jailbreak (Version – v6.1.1)
Unc0ver is the most popular iOS 13 Jailbreak method in the world. You can Jailbreak all latest iPhone and iPad models using Unc0ver and install Cydia. Now it supports up to iOS 13.6.1 Jailbreak.
4) Checkra1n (version – 0.12.2 beta)
Checkra1n is the only semi-untethered jailbreak method supporting all iOS 13 versions including iOS 13.5.1, iOS 13.6 & iOS 13.6.1. Checkra1n Jailbreak is somewhat more complicated than Unc0ver, Odyssey and Hexxa plus jailbreak repo extractor.
5) Flux 6 Jailbreak (version – 6.0.0)
Flux Jailbreak was released recently to jailbreak iOS 13 to iOS 13.6.1 versions. This jailbreak tool is based with Odyssey IPA. You can use this Semi Untethered jailbreak for all the iOS 13 versions.
6) Hardware Jailbreak
Hardware Jailbreak is different from software Jailbreak. You can modify default iPhone hardware features using some hardware gadgets. Hardware jailbreak is compatible with all iOS 13 versions including iOS 13.6 / iOS 13.6.1. But unfortunately, Hardware Jailbreak is not available for iPads and the latest iPhone models such as iPhone 11, iPhone XS, iPhone X etc.
1. Hexxa Plus (version 5.49 )
Hexxa Plus v 5.49 is the most popular Jailbreak repo extractor for all iOS 13 versions including iOS 13.5.1, iOS 13.6 and iOS 13.6.1. It is different from semi-untethered and untethered Jailbreak. You can install awesome Jailbreak and non-jailbreak tweaks, themes, and apps via Hexxa Plus.
Compatible iOS versions – Hexxa plus updated for iOS 13.5.1, iOS 13.6, and iOS 13.6.1. But It is also compatible with the following iOS versions.
iOS 13, iOS 13.1, iOS 13.1.1, iOS 13.1.2, iOS 13.1.3, iOS 13.2, iOS 13.2.2, iOS 13.2.3, iOS 13.3, iOS 13.3.1, iOS 13.4, iOS 13.4.1, iOS 13.5, iOS 13.5.1, iOS 13.6, iOS 13.6.1
Compatible device – Hexxa Plus is compatible with the following devices.
iPhone 6S / 6S Plus, iPhone 7 / 7 Plus, iPhone 8 / 8 Plus, iPhone X, iPhone XS / XS Max, iPhone XR, iPhone 11, iPhone 11 Pro, 11 Pro Max,
iPad Air 2G, iPad Air 3G, iPad (5th gen), iPad (6th gen), iPad (7th gen), iPad Mini 4, iPad Mini 5, iPad Pro (1st gen), iPad Pro (2nd gen), iPad Pro (3rd gen)
New features of Hexxa Plus iOS 13.6 / iOS 13.6.1 Jailbreak repo extractor
Hexxa Plus introduced new iOS 13.6 / iOS 13.6.1 jailbreak app’s shortcuts as repo extractors. Below has listed the most valuable iOS 13.6 / iOS 13.6.1 jailbreak app’s shortcuts. Make sure to allow the “Allow Untrusted Shortcuts” toggle before installing shortcuts. Just go to the Settings tab and open the Shortcuts to change settings. Now, you can install any of the following Shortcuts into iOS 13 devices up to iOS 13.6.1.
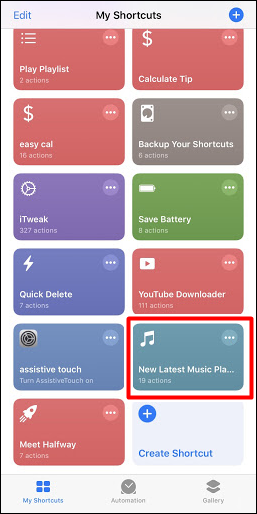
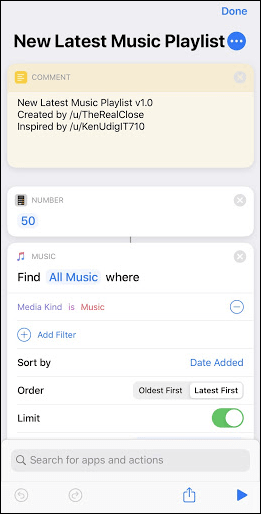
- New Music Playlist
You can install New Music Playlist adding the following iOS 13.6 / iOS 13.6.1 Jailbreak repo from Hexxa Repo Extractor.
New Music Playlist is a very useful tweak for Music lovers. It can add the most recent upto 50 songs to the library with a new playlist name and date range. There are many options under the New Music Playlist such as Search, sort by, order, limit, create playlists and more.
- Meet Halfway
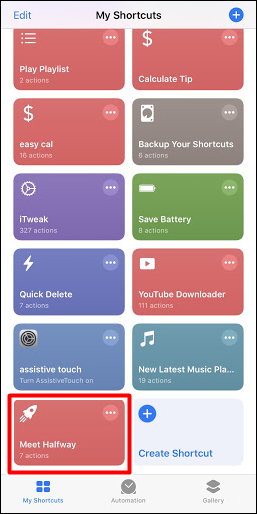
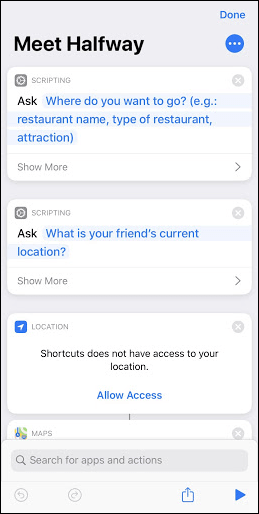
Meet Halfway is another cool feature of Hexxa iOS 13.6 / iOS 13.6.1 Jailbreak repo extractor.
You can install Meet Halfway shortcut to your iOS 13.6 / iOS 13.6.1 devices using the following repo.
Meet Halfway can be used to create a shortcut between your location and another location which you want to meet other contact. It can manually set the location or select the other contact’s address using Map. After setting the two places, you can find the best midpoint place (halfway point place) to meet each other between two locations. It helps to find the distance, location and time for both persons using the Map app.
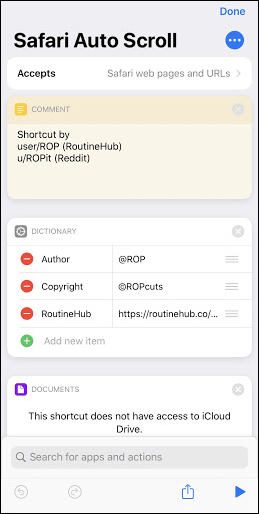
- Safari Auto scroller
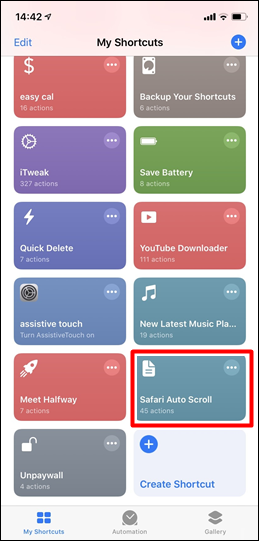
It is a perfect feature for readers. You can browse and read articles in Safari hands free with automatic scrolling.
Using the following repo to install Safari Auto Scroller to your iOS 13.6 / iOS 13.6.1 iPhone / iPad through Hexxa Plus Jailbreak Repo extractor.
Open Safari. Visit the website which you want to read. Then open the Share Sheet. Tap the Safari Auto Scroll. Then follow the instructions to allow access. This Safari Auto Scroller shortcut app has an option to customize auto scroll as your choice. Just set the scroll speed time as your choice. This shortcut never transfers any data. It just asks to access to run the JavaScript, which you want to allow the automatic scrolling.
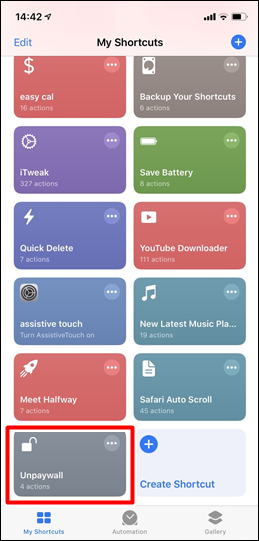
- UnPaywall
UnPaywall is the most popular 3rd party feature for iOS 13.6 / iOS 13.6.1 running iPhones or iPads.
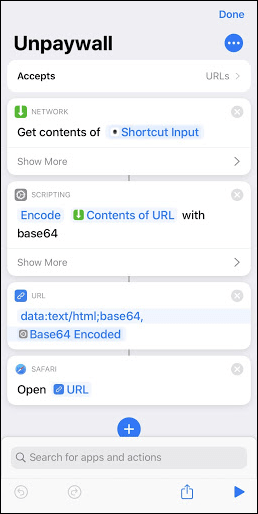
UnPaywall gives a chance to bypass paywalls in Safari. It helps to read any article on your iPhone’s Safari web browser. Using The shortcut of this app, it is very easy to get an unpaywall option. Add the following repo to your Hexxa Jailbreak repo extractor to install UnPaywall
Just choose and install the Unpaywall shortcut to your iOS 13.6 / iOS 13.6.1 device from the given shortcut list. Then go to Safari and open the article that has paywall. Tap the Share icon, which is located in the navigation bar at the bottom of the screen. Then the article page will bring to the Share Sheet. Scroll down and find the Unpaywall shortcut from the installed shortcut list. Open it and click the OK button to activate the Unpaywall option. Now you can read articles without paywalls.
More info about Hexxa Plus
Hexxa Plus helps to install many third party jailbreak apps to iPhone or iPads running iOS 13 – iOS 13.6.1. It is a very easy method to install third party apps including Cydia and Sileo. Hexxa Plus never asks Cydia impactor or iTunes support to run it. It works properly on iOS 13 devices without breaking iOS system root and without avoiding Apple warranty.
Extracting repo is not a new method. It was released targeting iOS 12.2 first as Hexxa. Hexxa supported all the iOS 12 versions up to iOS 12.5.7 Jailbreak. Then it was developed adding more repos and released as Hexxa Plus targeting iOS 13 versions. The Hexxa Plus team has confirmed that it is supported on all iOS 13 running devices without any errors. However you will be missing system functionality because it does not break the system root.
2. Odyssey Jailbreak
Now Odyssey v1.2 release available for iOS 13 – iOS 13.7 jailbreak. Previously, it was released up to Jailbreak iOS 13.5 version. Odyssey will come with pre-installed Sileo. But it allows users to choose the package managers of Zebra, Installer, or Cydia if they don’t like the default installer. It has many installation methods to install Odyssey such as the Online, Wander, Jailbreak.app Altstore & Reprovision.
Compatible iOS versions: iOS 13, iOS 13.1, iOS 13.1.1, iOS 13.1.2, iOS 13.1.3, iOS 13.2, iOS 13.2.2, iOS 13.2.3, iOS 13.3, iOS 13.3.1, iOS 13.4, iOS 13.4.1, iOS 13.5, iOS 13.5.1, iOS 13.6, iOS 13.6.1
Compatible device – A9 to A13
iPhone XS, iPhone XS Max, iPhone XR, iPhone 11, iPhone 11 Pro, iPhone 11 Pro Max, iPhone X, iPhone 7/7 Plus, iPhone 8/8 Plus, iPhone 6S/6S Plus, iPhone SE
iPad Air 2G, iPad Air 3G, iPad (5th gen), iPad (6th gen), iPad (7th gen), iPad Mini 4, iPad Mini 5, iPad Pro (1st gen), iPad Pro (2nd gen), iPad Pro (3rd gen)
Step Guide (Online method)
Step 01 – Visit this page from your iPhone or iPad’s safari browser
Step 02 – Tap the above odyssey download button.
Step 03 – Once finished the installation, trust the odyssey app before opening it. Go to Settings > General > Profile and Device management > Trust the Odyssey app
Step 04 – Open the Odyssey app & tap on the jailbreak button. Let it complete the Jailbreak exploitation process.
Step 05 – Finally you can see the Sileo app on your device homescreen.
It has a computer required Cydia impactor alternative IPA side loading method and altstore method to complete the Jailbreak process. Find the guides from and more information from Odyssey Jailbreak page.However, these methods are a bit complicated and the Online method is the easiest method.
Wander Method – The official Odyssey jailbreak installer
Now it has introduced the Wander add-on for Apple’s Shortcuts app to install the Odyssey jailbreak. Wander shortcut is developed by Burrito BurritoSOFTWARE. Wander installer lets you download Odyssey and fully compatible with AltStore, ReProvision, or save it to the Files app.
Also, compatible with Jailbreaks.app. Jailbreaks.app is a free 3rd party AppStore developed by iCraze @iCrazeiOS. It will let you install the most popular jailbreak tools without a computer.
How to add Wander to the Shortcuts app & install Odyssey
Step 01 – Download the Shortcuts app in Apple’s App Store for free.
Step 02 – Make sure that the Allow Untrusted Shortcuts option is turned on. (Go to Settings → Shortcuts → Allow Untrusted Shortcuts option)
Step 03 – Go to Odyssey official site from your device Safari browser, tap on the Add Shortcut button.
Step 04 – It will be redirected to a routinehub.co web page & tap on the Get Shortcut button.
Step 05 – Tap on the red Add Untrusted Shortcut button from going down through the popups. Finally, tap on “Done.”, Now you have set up wander Shortcuts.
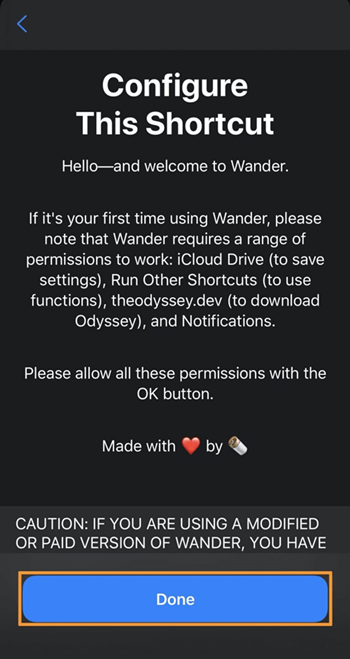
Step 06 – Tap on the Wander shortcut, Then tap OK to access to iCloud Drive, App will now display the welcome page, tap on the blue Done button, finally ask for permission to use other shortcuts, Tap OK button to confirm.
Step 07 – Once configure the wander on your device, prompted with the option to install or update the Odyssey jailbreak.
Step 08 – It will ask you to install Odyssey with AltStore, ReProvision,Jailbreaks.app or any other
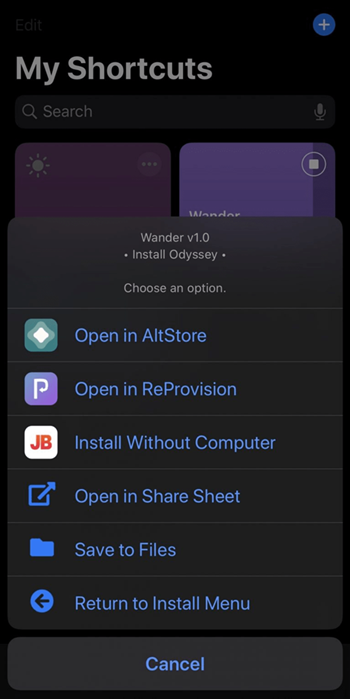
Step 09 – Select the installation option from the menu and once you tap any option it will download the Odyssey jailbreak app to your device. Then complete the Jailbreak process opening odyssey app.
3. Unc0ver Jailbreak
The Unc0ver Jailbreak tool is available for iOS 13 – iOS 13.6.1. Jailbreak. Recently, the Unc0ver team released version 8.0.0 adding Unc0ver support up to iOS 14.8 jailbreak.
It has Uncover jailbreak for Mac & Windows with AltStore or usual Cydia Impactor methods to download Unc0ver. You must download AltStore for your MacOS or Windows. However, Unc0ver Windows Jailbreaking is a somewhat advanced method for experts. Also, use Reprovision to install unc0ver permanently.
Compatible iOS versions: iOS 13, iOS 13.1, iOS 13.1.1, iOS 13.1.2, iOS 13.1.3, iOS 13.2, iOS 13.2.2, iOS 13.2.3, iOS 13.3, iOS 13.3.1, iOS 13.4, iOS 13.4.1, iOS 13.5, iOS 13.5.1, iOS 13.6, iOS 13.6.1
Compatible device : Unc0ver compatible with All following device models.
iPhone XS, iPhone XS Max, iPhone XR, iPhone 11, iPhone 11 Pro, iPhone 11 Pro Max, iPhone X, iPhone 7/7 Plus, iPhone 8/8 Plus, iPhone 6S/6S Plus, iPhone SE
iPad Air 2G, iPad Air 3G, iPad (5th gen), iPad (6th gen), iPad (7th gen), iPad Mini 4, iPad Mini 5, iPad Pro (1st gen), iPad Pro (2nd gen), iPad Pro (3rd gen)
Altstore Method for Mac users
Download – AltStore
Step 01 – Unzip the downloaded file and move AltStore to your Applications folder.
Step 02 – Run the Alt Store>Tap on the AltStore icon in the Menu Bar > then Install Mail Plug-in option > Open the Mail app > Tap on Mail → Preferences in the menu bar.
Step 03 – Now open the General tab in mail preferences > Tap on Manage Plug-ins >check AltPlugin, and apply and restart Mail.
Step 04 – Connect your iPhone or iPad to the Mac. Tap on AltStore in the menu bar. Go to Install AltStore > Tap your device. Provide your Apple ID & Password when needed and tap on install.
Step 05 – Now go to your device Settings → General → Device Management and tap on your Apple ID.
Step 06 – Download Uncover IPA from official site & AltStore will install the Unc0ver app. Once done,
Open unc0ver app and complete the Jailbreak process.
Note : You can complete the Uncover process if you have an Apple developer account, follow the same steps on Windows Cydia impactor guide.
Altstore Method for Windows users
Step 01 – Install iTunes according to device and Download AltStore according to operating system from above buttons.
Step 02 – Extract All from the downloaded zip file. Double click “Setup.exe”. Follow the AltStore on screen instructions.
Step 03 – Tap the Windows key, then type “AltServer,” and open the application.
Step 04 – Now tap on the arrow placed in the taskbar. Tap the AltServer Logo. Go to options > Install AltStore > select your iOS device > provide your Apple ID and password.
Step 05 – Now Trust the AltStore. to do that go to your iOS device Settings -> General -> Device Management.
Step 06 – Go to unc0ver official site and download the latest Unc0ver tool version. Open the IPA file using AltStore. When asked to login credentials, Enter same ID & Password.
Step 07 – Now, AltStore will install the Unc0ver app to your device. You can go ahead with the Unc0ver Jailbreak process.
You can also use the Cydia Impactor method to Jailbreak your iOS 13 – iOS 13.6.1 running device using Unc0ver.
Cydia Impactor Method for Windows users
Note: It should require an Apple developer account to use this method.
Step 01 – Download Uncover IPA and Cydia Impactor according to OS from above buttons.
Step 02 – Now Connect your device to the Computer.
Step 03 – Drag the downloaded uncover ipa file into the Cydia Impactor window.
Step 04 – Provide your Apple ID and password to sideload the IPA to your device.
Step 05 – Wait until the side load process. Then go to your device Settings -> General -> Device Management and tap on your Apple ID and Trust the unc0ver.
Step 06 – Now you can run the Uncover app located on your device homescreen. Go ahead with the iOS 13 – iOS 13.6.1 Jailbreak process.
Unc0ver Jailbreak for Linux
Linux users are able to use the Unc0ver Linux jailbreak with Cydia Impactor method to complete the jailbreak process for iOS 13 to iOS 13.6.1 versions. Just download the Unc0ver IPA and Cydia Impactor tool according to the Linux OS. Then you can follow the below guide to jailbreak iOS 13.6.1 – iOS 13, if you are using the Linux computer.
Step 01 – Download Uncover IPA and Cydia Impactor tool according to OS. Use the above link to download it.
Step 02 – Connect your iPhone or iPad with Linux Computer.
Then you can use the same Windows guide to complete the Linux + Unc0ver jailbreak process. Just drag the Unc0ver IPA into the Cydia Impactor window. Provide Apple ID and the Password to begin the sideload. Once finished, go to device settings -> General -> Device Management and tap on your Apple ID and Trust unc0ver. Finally, you can launch the Unc0ver app to complete the jailbreak process.
Unc0ver iOS 13.5.5 beta 1 Jailbreak fixed via iOS 13.6 beta 2
Apple released iOS 13.6 beta 2 renaming iOS 13.5.5 beta 1. A couple of weeks ago, Apple released iOS 13.5.1 as well as iOS 13.5.5 beta. They have released the iOS 13.5.1 to fix the vulnerabilities which is caused to develop Unc0ver up to iOS 13.5 Jailbreak. Apple has patched the Unc0ver Jailbreak via this iOS 13.5.1 release.
Then Apple released iOS 13.6 beta 2. The main reason for this 13.6 beta 2 release is, Unc0ver added the iOS 13.5.5 beta 1 jailbreak support only for Windows & Mac users only. Apple patch iOS 13.5.5 unc0ver Jailbreak vulnerability releasing iOS 13.6 beta 2. The official site offers this iOS 13.5.5 beta 1 IPSW download file too.
If anyone wants Unc0ver Jailbreak for iOS 13.5.5 beta 1, you can download both iPSW and Unc0ver v5.2.0 tool from Unc0ver.dev official site.
Also, Pwn20wnd has confirmed it and informed that do not update iOS version to iOS 13.5.1 or later if you want Unc0ver jailbreak. At this time Hexxa Plus is the only iOS 13.5.1, iOS 13.6, iOS 13.6.1 & iOS 13.7 Jailbreak solution for all users. If you are a Windows, Linux or iOS user, you can install jailbreak apps for iOS 13.5.1 using Hexxa Plus.
4. Checkra1n Jailbreak
Checkra1n is a very rare permanent (but semi-tethered ) Jailbreak. Now it has added Jailbreak support for all iOS 13 versions on A5-A11 devices (except A12/A13 devices.) Also, it should be compatible with all current and future iOS versions according to the nature of Checkra1n Jailbreak.
Version Compatibility
iOS 13, iOS 13.1, iOS 13.1.1, iOS 13.1.2, iOS 13.1.3, iOS 13.2, iOS 13.2.2, iOS 13.2.3, iOS 13.3, iOS 13.3.1, iOS 13.4, iOS 13.4.1, iOS 13.5, iOS 13.5.1, iOS 13.6, iOS 13.6.1
Device Compatibility
iPhone 6S / 6S Plus, iPhone 7 / 7 Plus, iPhone 8 / 8 Plus, iPhone X, iPhone XS / XS Max, iPhone XR, iPhone 11, iPhone 11 Pro, 11 Pro Max
iPad Air 2G, iPad Air 3G, iPad (5th gen), iPad (6th gen), iPad (7th gen), iPad Mini 4, iPad Mini 5, iPad Pro (1st gen), iPad Pro (2nd gen), iPad Pro (3rd gen)
checkra1n is not supported by the following devices.
Checkra1n for windows
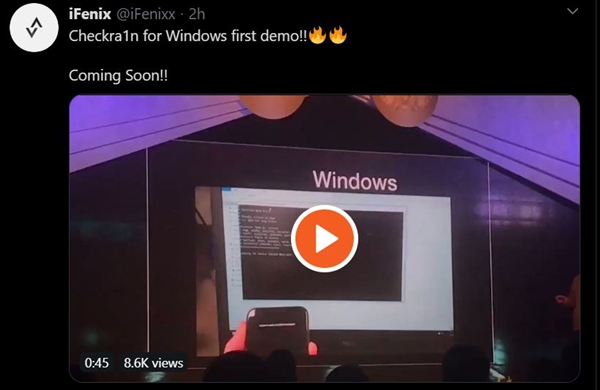
Checkra1n windows support officially added soon. Already they have demonstrated it. Once it is released, it will definitely be compatible with iOS 13.6 and iOS 13.6.1 Jailbreak from iOS 13, hence CheckRa1n support for all these versions.
Webra1n for Checkra1n
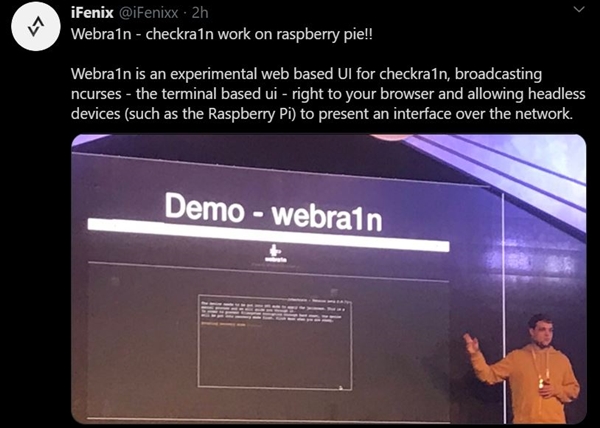
Checkra1n team is going to introduce a web interface called webra1n for checkra1n. It is designed for a raspberry pi. Webra1n for Checkra1n will be supported with all CheckRa1n supported versions.
Ra1nUSB – Checkra1n alternative for Windows
Ra1nUSB is a Windows Alternative for Checkrain. You can use the Ra1nUSB method to Jailbreak iOS 13 – iOS 13.6.1 on Windows operating system. No hints about other versions and this should be compatible up to Jailbreak iOS 13.7 with Ra1nUSB.
Go to the Ra1nUSB Jailbreak page to download Ra1nUSB. Download links/ guides and all the details available.
Ra1nBox portable checkra1n jailbreak using Linux Board
Portable Checkra1n jailbreak also known Checkra1n jailbreaking on the go is possible with Ra1nbox now. Ra1nbox is a tiny computer which is running ra1nbox software.
The developer Fidelity has shown a sample of jailbreaking an iPhone X running iOS 13.3 with NO PC Ra1nBox portable checkra1n jailbreak method. According to the developer it is possible to jailbreak iOS 12.3 to iOS 13.3.1 on your A5 to A11 iDevices. (Including iPhone 5S to iPhone X) Also, it might work with iOS 13.4 / iOS 13.4.1 / iOS 13.5 / iOS 13.5.1 / iOS 13.6 / iOS 13.6.1 too.
It needs a Checkra1n support device, micro USB power adapter, nano PI neo 2 Linux board, Ra1nbox software and regular lightning cable to complete the jailbreak process.
Here is the video guide tutorial.
Bootra1n for CheckRa1n – Boot from USB straight into Linux
Foxlet released bootra1n for Linux to boot checkra1n on any PC. You just need to have a USB flash drive (512MB or higher.) This is compatible with iOS 13 – iOS 13.6.1.
Here is the download links & step guide to run Bootra1n jailbreak.
Get iOS 14 widgets to iOS 13 Jailbroken device with Comet
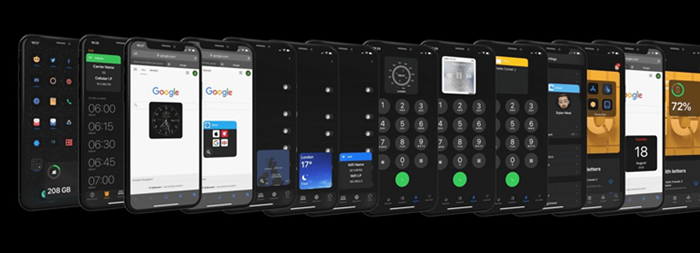
It has introduced the cool homescreen widgets with iOS 14 features on WWDC 2020. You can get these features iOS 14, no need for Jailbreak iOS 14.
If you need these cool features on older iOS 13 devices, you should Jailbreak your iOS 13 device. Then you can get these features on your iOS 13 Jailbroken device without upgrading to iOS 14.
iOS developer Dylan West (@iOSthemem0d) has released a new Jailbreak tweak as Comet. Comet Inspired by iOS 14 widgets called smart stack. However, it is not available on SpringBoard. You can access Lockscreen, springboard and in applications using activator gesture. You can bring comet widgets on Storage, Carrier, Clock, Safari, Maps, Weather, Wi-Fi, Compass, Music, Notes, iCloud, Favorite Apps, Calendar & Battery.
Once you install the Comet, it adds a preference pane to the Settings app to customize & configure the tweak and its widgets.
5. Flux 6 Jailbreak
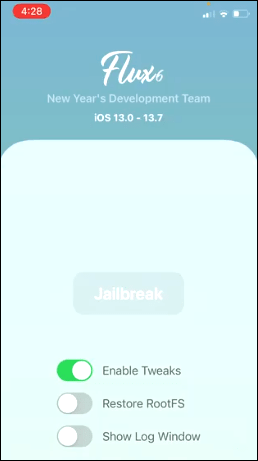
Newly added Flux 6 Jailbreak tool available to jailbreak all iOS 13 versions. That means iOS 13 – iOS 13.6.1 jailbreak including iOS 13.7 too. The Flex Jailbreak developer confirms that this jailbreak is based with Odyssey jailbreak. Just download Flux Jailbreak v6.0.0 IPA from the following button. Then you can use the same Odyssey IPA sideload method to complete Flux 6 jailbreak for Sileo or Cydia.
6. Hardware Jailbreak
Hardware Jailbreak is a process that adds features to iPhones with adopted gadgets. This is still not famous among iOS users because of a lack of knowledge and there are not many hardware programmers.
However, Sayonir team did hardware programming for 3rd party Gadgets for a few years. Now Ru$za & Pangu8 developers are also interested in this hardware programming for the latest iPhones.This makes a big difference on your iPhone. Currently, changing Apple backside Logo color, Increase the IPhone Memory and Improve The Battery Capacity with adopted hardware are most concerned.
More iOS 13 – 13.6.1 Jailbreak Tools
Bregxi
Bregxi is another Repo extractor. Bregxi is an easy online jailbreak app installation process. If you are familiar with adding source on jailbroken devices through Cydia, this is the same. But, not that complicated. Bregxi was introduced for iOS 12.3 Jailbreak for the very first time. Now this is compatible with the iOS 13 – iOS 13.6 jailbreak. Bregxi team updated Bregxi for iOS 13.6.1 and confirmed that it works properly on iOS 13.6.1.
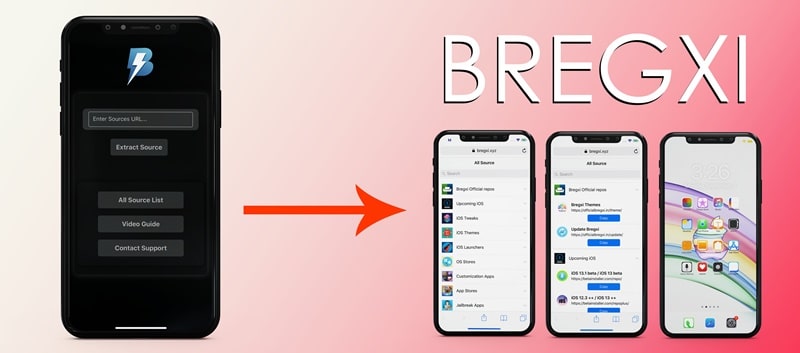
Once you install Bregxi on your device you can install iOS 13 – iOS 13.6.1 Jailbreak tweaks. There are thousands of sources to install Jailbreak tweaks, themes, and more third party apps for device customization.
Blizzard Jailbreak
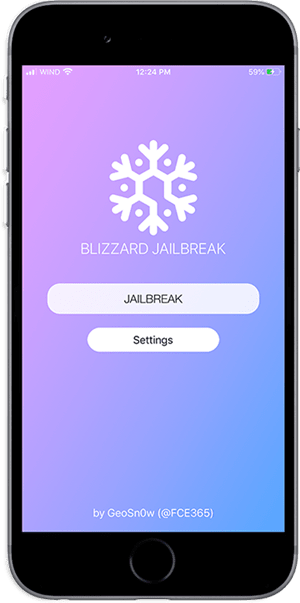
Blizzard Jailbreak is a new open-sourced Jailbreak up to iOS 13.5. This tool is released by GeoSn0w. It has used Jake James, Pwn20wnd 7 Electra Team works for this project. Initially it is planned to be released for iOS 11 – iOS 11.4.1. Then it will update for iOS 12 – iOS 13.5 Jailbreak. Also, this is supported with all device models including A12 / A13.
Note – Still this Blizzard Jailbreak not available to download. You can get Blizzard Source files only.
Fugu Jailbreak for iOS 13 – iOS 13.3.1 (open source tool)
Fugu is the first open source jailbreak based on the checkm8 exploit. It was released by Linus Henze for Jailbreak iOS 13 – iOS 13.3.1. If you are a developer you can try this method.
Fugu jailbreak not available for iOS 13.4 – iOS 13.6.1. According to developers Fugu Jailbreak will not be updated to iOS 13.6, iOS 13.6.1.
This is under development and currently iPad Pro (2017) and iPhone 7 are the only supported devices. More Fugu Jailbreak compatible devices will be added soon. Also, you can install Sileo or Cydia, tweaks using fugu, but sometimes it may not work because the fugu is still in the development stage.
Fugu components
Once you are exploiting the iPhone using the macOS app based Checkm8 exploit, it will upload the following component.
iStrap Loader – This Kernel bootstrapper you can see during boot. Patches the kernel, injects boot arguments and injects shellcode into the kernel.
iStrap – iStrap is a small shell code. It is patched iBoot and loaded with iStrap after the iBoot is completed.
iDownload – This small application running on your iPhone installed during boot and launched instead of launchd.
Also, we could find concept videos for Fugu. Watch the following video to know how it works.
Chimera Jailbreak
Coolstar released Chimera13 open source project to Github a few times back. Also, he released Chimera1n script to bring checkra1n bootstrap on the checkra1n jailbreak with the Chimera bootstrap. It will help you to get Sileo on iOS 13 – iOS 13.4.1 CheckRain compatible devices. This may work with iOS 13.5, iOS 13.5.1, iOS 13.6, iOS 13.6.1 too hence checkra1n can not be fixed via software update.
Before this, Cool star published a screenshot of Chimera Jailbreak working on iPadOS 13. Further previously he created a poll “Should I release Chimera13 for 13.0 – 13.3 on A9-A11 so people can see how an iOS 13 semi-untether is supposed to be done?” on twitter. According to the results, Chimera Jailbreak for iOS 13 will support A9 through A11 devices.
However Electra team did not release Chimera jailbreak for iOS 13, iOS 13.1, iOS 13.1.1, iOS 13.1.2, iOS 13.1.3, iOS 13.2, iOS 13.2.2, iOS 13.2.3, iOS 13.3, iOS 13.3.1, iOS 13.4, iOS 13.4.1, iOS 13.5, iOS 13.5.1, iOS 13.6 or iOS 13.6.1 version yet.
TaigOne
TaigOne is iOS 13 – iOS 13.6.1 Jailbreak alternative developed by the Taig9 team. They offer both computer and online methods for TaigOne. They called it as Taigone jailbreak tool finder, Taigone jailbreak app installer, Taigone jailbreak app & repo.
TaigOne mainly promotes Yiti Apps (Hundreds of Paid apps for FREE), Li Tweaks (Famous Ying and Pong), InCar (New CarPlay Tweak). You can access their services by purchasing TaigOne Packages. There are packages starting from $9.99 to $19.99 as Taigone-Lite, Taigone-Classic, Taigone-Royal. Also, you can receive TaigOne premium badges through the Taigone free package.
Tiqu ++
Tiqu++ is a repo installer. It will let you add repos same as in a jailbreak but without a jailbreak. This is specially released for iOS 13. Now it is upgraded as a Tiqu+repo installer for iOS 13.1 – iOS 13.6.1 jailbreak. Tiqu ++ is available to purchase at $3 from litweaks official website. Tiqu++ developed by the famous jailbreak hacker Li Yuan Ying.
C1nUSB
C1nUSB is iOS 13 – 13.3 Checkra1n based Jailbreak that you can Jailbreak your device online.
We found an Online Checkra1n Jailbreak tool called c1nusb Jailbreak from the internet. It seems a very easy method to transfer files using iPhone Flash Drive through their C1nusb site. So, you can complete the iOS 13.3 Jailbreak process without using Computer. They did not mention the iOS 13.3.1, iOS 13.4, iOS 13.4.1, iOS 13.5, iOS 13.5.1, iOS 13.6 or iOS 13.6.1 versions.
Here is the extracted Video of Checkra1n Online Jailbreak.
According to the video, you should have an iPhone Flash Drive with 8 GB or above Capacity to complete the C1nUSB Online Jailbreak process. It should transfer the files through c1nusb site using MAC or Windows PC to iPhone Flash Drive. Then using Flash drive you can complete the Jailbreak process online.
However, we don’t know much about this Checkra1n Jailbreak online method. But we can find the details from famous Jailbreak sites such as Reddit too. If it works perfectly, it is a very useful method because it can complete the whole Checkrain Jailbreak process Online.
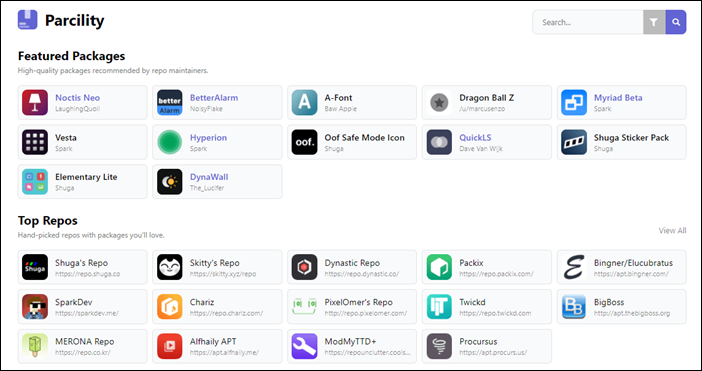
Parcility web-based repository browser – Find your favorite iOS 13 Jailbreak repos
Parcility is a website & API for browsing your favorite jailbreak repos, packages & developers. This project was brought to you by Zenith & team of developers. Once you Jailbreak iOS 13 – iOS 13.6.1 with Uncover, Odyssey or Checkrain you can find High-quality packages recommended by repo maintainers.
Parcility comes with many features. Several features are given below.
Browse packages from 600+ repositories
Search a database using several variables.
Most popular packages / repositories are highlighted in the home page.
View all the packages by a specific author and the repositories
Full-featured tweak depiction pages
Download .DEB files of free packages directly from the web
View package price information directly from the web
Inferius – for downgrading to older iOS 13 versions
Inferuris released for creating & restoring from custom IPSWs via checkm8 exploit. This is written in Python. So, you can downgrade to the previous iOS 13 versions which is no longer being signed by Apple. This is compatible with all 64-bit devices that checkm8 compatible. Currently, Inferuris is only supported by MacOS only and a Linux version may be released in future. Inferius Developed by @marijuanARM.
Create a custom IPSW with Inferius using the following commands.
pip3 install -r requirements.txt
./inferius.py -d ‘device’ -i ‘iOS Version’ -f ‘IPSW’ [-v]
You need to restore your device with the created IPSW with Restituere.
./restituere.py -d ‘device’ -i ‘iOS version’ -f ‘IPSW’ [-v]
Please note – You need to boot your custom IPSWs loaded device with PyBoot or ra1nsn0w every time hence not untethered.
*PyBoot – Tethered booting Script for Checkm8 compatible iOS devices by Matty.
*Ra1nsn0w – A tethered booter for Checkm8 compatible iOS devices by Tihmstar
Popular iOS 13 to iOS 13.6.1 Jailbreak apps / tweaks
- PowerSettings
Powersettings is one of the most popular Jailbreak features for iOS 13.5 / iOS 13.5.1 / iOS 13.6 / iOS 13.6.1 running iPhones / iPads. When you install PowerSettings Jailbreak app on your device, it creates a new tab on your settings as power options. You can easily change the settings with one tap using PowerSettings. PowerSettings tweak gives quick, simple and easy power options to the Settings app.
- SettingWidgets
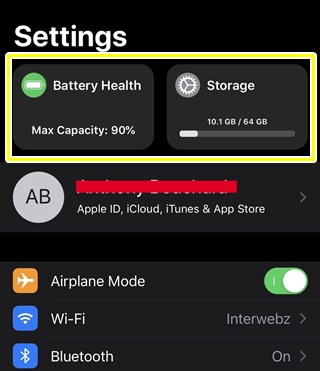
SettingWidgets is a perfect iOS 13.5 Jailbreak tweak. After adding this tweak, users can get informative widgets to the settings front page such as Battery, Storage, Cellular and WiFi. First, complete the jailbreak process using Unc0ver or Odyssey jailbreak tool. Then open Cydia or Sileo app managers. Add https://repo.dynastic.co/ repo to your device. Now, you can install SettingsWidgets tweak to your iOS 13.5 device.
- HomeSize
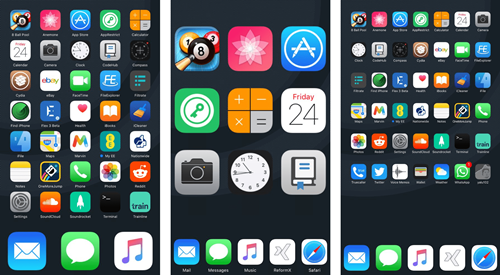
HomeSize is a iOS 13.6.1 jailbreak tweak to customize Home bar size length and width. Users can hide the Home bar using this. You can install HomeSize jailbreak tweak for iOS 13 to iOS 13.6 devices as well. Find the HomeSize jailbreak tweak from BigBoss repo.
- PowerModule
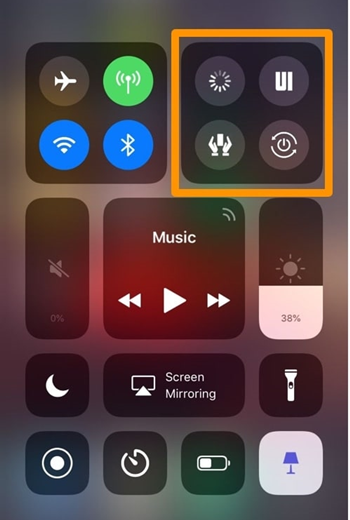
PowerModule is a jailbreak tweak to give many toggles to the Control Center such as Respringing, clearing UI cache, entering safe mode, rebooting, locking the screen. After installing PowerModule tweak, it gives additional controls to the settings app. This tweak works fine as iOS 13.5, iOS 13.5.1, iOS 13.6 and iOS 13.6.1 jailbreak tweak for jailbroken iDevices.
iOS 13.6 Jailbreak Approaches
iOS 13.6.1 kernel read/write primitives on iPhone Pro Max demonstrated
Security researcher @08Tc3wBB demonstrated new custom built kernel read/write primitives on iOS 13.6.1 running iPhone Pro Max. This is a completely different method from tfp0 exploit. However, work is still going on and he will publicize the exploit once appropriated. If it is released, could be used to develop iOS 13.6.1 Jailbreak like unc0ver or brand new one.
iOS 13.6.1, iPhone 11 Pro Max, using custom built kernel read/write primitives, completely got rid of the tfp0 method. I’ll make it public when it’s appropriate. #JAILBREAK pic.twitter.com/3mwIVsrN1s
— 08Tc3wBB (@08Tc3wBB) August 15, 2020
tfp0 exploit supported on iOS 13.6
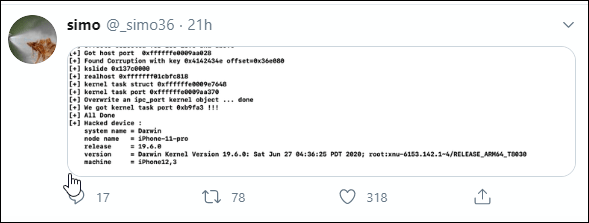
Security researcher @_Simo36 announced that tfpo exploit works with the latest iOS 13.6 version. That means iOS 13.6 is vulnerable. tfpo exploit used to create many famous jailbreaks such as Unc0ver, Chimera, Electra. So if the tfp0 exploit works with iOS 13.6 we can expect semi-untethered jailbreak like unc0ver for iOS 13.6 very soon. However, this is software based jailbreak, so it can be patch releasing a new iOS version by Apple.
Cuck00 new kernel exploit released up to iOS 13.3
A XNU/IOKit info leak 1day killed in iOS 13.3.1 beta 2.https://t.co/M1Iw69a53o
— @siguza@mastodon.social (@s1guza) January 18, 2020
Siguza released a new exploit through XNU/IOKit bug built around mach port. Actually this is a very old bug and it exists in the very first version of XNU. He gave an unofficial name to the bug as Cuk00. This bug was fixed in iOS 13.3.1 beta 2. However, a fully functional exploit up to iOS 13.3 is available on GitHub. Cuck00 exploit may be compatible with latest iOS 13.6 too.
iOS 13.6 Jailbreak Checkra1n 0.10.2 Windows Method by Justatech
We found another checkra1n windows alternative method by Justatech. Here is the simple guide to try that iOS 13.6 Jailbreak Checkra1n 0.10.2 Windows method.
- Download the RUFUS to make bootable USB. (Download it from iamjustatech.blogspot)
- Open the RUFUS from Checkra1n 0.10.2 by JustaTech and make it bootable. (only use the rufus, provided on site because it has important linux sys files that are important for make usb bootable)
- You should connect to the Internet while making the Bootable USB. Because when you use the RUFUS tool for the first time, it will download the required Libraries files to create bootable USB.
Once completed the process, restart your Windows PC and Choose following options.
Boot from UEFI (For new PC with UEFI support)
Boot from legacy BIOS (for Old PC, No support of UEFI)
It works on both AMD / INTEL [ 64/32 Bits] , MACOS , LINUX OS as well.
- Select your USB and wait for 5 seconds. It will automatically load the Checkrain.
How to jailbreak iOS 13.6 using Tweak box
Tweak box is another popular app to download 3rd-party apps and tweak. Now it has fully updated for iOS 13.6 Jailbreak. Here is a simple instruction to jailbreak iOS 13.6 using Tweak box.