Check a Certificate Thumbprint
This tool fetches the SSL certificate of a given domain or host and calculates SSL certificate fingerprint hashes.
What is an SSL, and why do I need an SSL certificate?
Even though, with time, Tech companies give more importance to user privacy and security. However, today, most internet users still believe that current laws are not enough to protect their rights.
The SSL certificate is the one that enables the website to redirect from HTTP to HTTPS.
SSL stands for Secure Sockets Layer; it’s a security technology that layers a secure connection between a web browser and web server and ensures that data transfer remains private. The SSL Certificate is also called TLS (Transport Layer Security).
You will need to install an SSL certificate on your web server to ensure that the data connection between your web server and web browser remains secure.
An SSL is a file hosted on a website origin server that contains key pair: a public key and private key. These keys work together to create an encrypted connection. The SSL certificate also includes the «subject,» which is the identity of the certificate/website owner.
Today, if you want to make your website look legitimate and trustworthy, you want to boost your conversions, sales, leads, revenue, customer loyalty, and satisfaction. It would help if you had an SSL certificate installed on your website’s server.
Especially, suppose you have an e-commerce store selling something online that requires user/customer’s personal information. In that case, you must have an SSL certificate to protect and encrypt the user’s data.
What is an SSL certificate thumbprint?
An SSL certificate thumbprint, also known as an SSL certificate fingerprint, is a hash of a certificate calculated on all certificate’s data and its signature.
The thumbprints are usually implemented with cryptographic hash functions. They are generally used as unique identifiers for certificates, configuration files, applications when making trust decisions and displayed in interfaces.
How is SSL certificate fingerprint calculated?
The SSL certificate thumbprint/fingerprint is a digest (hash function) of a certificate in x509 binary format. Different algorithms, such as SHA1 (for Microsoft Internet Explorer), can calculate it.
How to find SSL certificate thumbprints/fingerprints?
It’s easy to find the thumbprints/fingerprints of an SSL certificate by using the web browser. The following instructions will help you in finding fingerprints of SSL certificate with several popular web browsers.
Chrome
- Click on the «lock symbol» located on the left side of the browser’s address bar.
- A pop-up dialog box will appear; click on «Certificate.»
- In the «Certificate» dialog box, click the «Details» tab.
- On the «Details» page, scroll down until the word «Thumbprint» is visible in the list and then click «Thumbprint.»
- You will get a thumbprint in the textbox below the list box.
Firefox
- Click on the «lock symbol» located on the left side of the browser’s address bar.
- A pop-up dialog box will appear. Click the arrow to the right of «Connection» to land on the Site Security page.
- At the end of the Site Security page, click on «More Information.»
- In the «More Information» page, the Security tab should be selected by default. If not, click on the Security tab.
- Click on the «View Certificate» button to view the Certificate Viewer dialog box.
- You will get a thumbprint at the bottom of the General tab.
Edge
- Click on the «lock symbol» located on the left side of the browser’s address bar.
- A pop-up dialog box will appear. Click the «View certificate» link.
- The certificate details will be available in the «Certificate Information» panel on the right side of the browser.
- In the textbox on the «Certificate Information» panel, scroll down until the fingerprint information is visible.
How to get an SSL Certificate Thumbprint by using an SSL Certificate Fingerprint Finder Tool?
To find the SSL Certificate Thumbprint, usually known as SSL Certificate Fingerprint, perform the following steps.
How to get SSL-Certificate sha1 fingerprint?
from Chromium source (net/cert/ev_root_ca_metadata.cc). If the Crypto?
When I try, I always get this
Which program can I use for this and what is the name of the command, to get this in crypto?
I will add a certificate as EV in firefox / chromium.
2 Answers 2
The SHA-1 fingerprint of a certificate is simply the SHA-1 digest value of its DER representation.
- If your certificate is in PEM format, you’d need to convert it in DER format first (this is a base-64 decoding).
- Then, use a SHA-1 digest algorithm (in whichever language you’re using) on this DER document.
For example, if you get the fingerprint with OpenSSL directly, you would get this:
If you convert the same certificate into DER and then compute its SHA-1 digest, you’ll get the same result:
( openssl . -outform DER produces a DER output on stdout, and sha1sum is a common utility for computing SHA-1 digests from its stdin.)
Примеры использования OpenSSL в Unix/Linux
При работе с SSL, нужно уметь работать с утилитой OpenSSL чтобы создавать, конвертировать, управляют SSL-сертификатами. В этой статье «Примеры использования OpenSSL в Unix/Linux» я буду говорить о примерах использования OpenSSL.
Некоторые из сокращений, связанных с сертификатами:
- SSL – Secure Socket Layer (Безопасный уровень сокета).
- CSR – Certificate Signing Request (Запрос на подпись сертификата).
- TLS – Transport Layer Security (Транспортный уровень безопастности).
- PEM – Privacy Enhanced Mail
- DER – Distinguished Encoding Rules
- SHA – Secure Hash Algorithm (Безопасный hash алгорит).
- PKCS – Public-Key Cryptography Standards (Стандарты шифрования публичных ключей).
Создание нового приватного ключа (Private Key) и Certificate Signing Request (CSR).
Команда выше будет генерировать CSR и 2048-битный RSA ключ. Если вы собираетесь использовать этот сертификат в Apache или Nginx, то вам необходимо отправить этот CSR файл в службу сертификации и они дадут вам подписанный сертификат в «der» или «pem» формате. После чего вы настроите его на веб-сервере Apache или Nginx.
Так же, можно использовать такой вариант:
Создание самоподписанного сертификата (Self-Signed Certificate).
Команда выше будет генерировать самоподписанный сертификат (self-signed) и 2048-битный RSA ключ. Я также использую алгорит шифрования — SHA256. Так как он считается наиболее безопасным в данный момент.
Замечание: По умолчанию, будет сгенерирован ключ толкьо на 1 месяц, если нужно создать на более длительное время — используйте опцию «–days», пример использования ниже.
Пример: Чтобы создать self-signed сертификат на 2 год, используйте:
Проверка CSR файла.
и вы получите информацию.
Проверка подписи (signature):
Кем(кому) был выдан сертификат:
Показать открытый ключ (public key):
Создать приватный RSA ключ (Private Key).
Чтобы это сделать, выполните:
Если вам просто нужно генерировать RSA закрытый ключ, вы можете использовать команду что выше. Я включил 2048 шифрование, для безопастности.
Удалить ключевую фразу (Passphrase) с ключа.
Если вы установили ключевую фразу для ключа, то при каждом старте веб-сервера (Apache/Nginx) вы должны будите вводить пароль. Если это вас злит, вы можете с легкостью удалить passphrase с RSA ключа.
Проверка приватного ключа (Private Key)
Если вы сомневаетесь в ключевом файле, вы можете использовать команду что выше для проверки.
Проверка сертификата (Certificate).
Если вы хотите проверить данные сертификата( CN, OU, и т.д.), то вы можете использовать команду, которая даст вам сведения о сертификате:
Команда довольна простая в использовании.
Проверка подписанного сертификата (Certificate Signer Authority).
Можно узнать много полезного.
Создать тестовый SSL сервер.
Команда OpenSSL s_server реализует общий SSL/TLS-сервер. Она должна использоваться только для целей тестирования. В приведенном ниже примере данный сервер прослушивает соединения на порту 8080 и возвращает отформатированную HTML страницу статуса, который включает много информации о ciphers:
Проверить хеш вашего сертификата.
Конвертирование сертификатов с DER в PEM формат.
Как правило, при покупке SSL сертификатов, его отдают вам в формате .der и если вам нужно использовать его в веб-сервере или .pem формате, вы можете использовать команду выше, чтобы преобразовать такие сертификаты.
Конвертирование сертификатов с PEM в DER формат.
В случае, если вам необходимо изменить .pem формат в .der:
Конвертирование CSR c DER в PEM формат.
Конвертирование сертификата и приватного ключа в PKCS#12 фотмат.
Если вам необходимо использовать сертификат с приложением Java или с любым другим, кто принимает формат PKCS# 12.
Совет: Вы можете включить «chain certificate» используя «-chain» опцию:
Создание CSR используя приватный ключ (private key).
Если вы не хотите создать новый секретный ключ, а хотите используя вместо существующего, вы можете с предыдущей командой.
Проверьте содержимое сертификата в PKCS12 формате.
PKCS12 — это двоичный формат, так что вы не сможете просматривать содержимое в блокноте или другом редакторе. Таким образом, вы должны использовать команду что выше, для просмотра содержимого файла формата PKCS12.
Конвертирование PKCS12 формата в PEM сертификат.
Получить SHA-1 отпечаток сертификата или CSR
Чтобы получить отпечаток SHA1 сертификата с использованием OpenSSL, используйте команду, приведенную ниже:
Чтобы получить SHA1 отпечаток пальца CSR с использованием OpenSSL, используйте команду, приведенную ниже:
Получить MD5 отпечаток сертификата или CSR
Чтобы получить отпечаток MD5 сертификата с использованием OpenSSL, используйте команду, приведенную ниже:
Чтобы получить MD5 отпечаток пальца CSR с использованием OpenSSL, используйте команду, приведенную ниже:
Тестирование SSL сертификата по URL.
Я использую это довольно часто для проверки SSL-сертификатов по URL с сервера. Это очень удобно для проверки некоторых деталей протокола, шифров и CERT.
Узнать версию OpenSSL
Поверка PEM сертификата на завершение (Expiration Date).
Проверка завершения SSL сертификата (Expiration Date) по URL.
Проверить поддержку SSL версии V2/V3 по URL.
Проверка SSL версии V2:
Проверка SSL версии V3:
Проверка TLS 1.0:
Проверка TLS 1.1:
Проверка TLS 1.2:
Проверка поддержки cipher для сайта по URL.
Какой алгоритм используется в сертификате (проверка).
Или, используя URL:
Получить сертификат по URL
Команда что ниже, сохранит сертификат в файл прямо по URL сайта:
Если веб-сервер имеет несколько сертификатов на один IP-адрес, то вам нужно будет сообщить OpenSSL, какой сертификат будет использоваться, пример ниже:
Вот и все, много полезностей и все в одной статье «Примеры использования OpenSSL в Unix/Linux».
Добавить комментарий Отменить ответ
Этот сайт использует Akismet для борьбы со спамом. Узнайте, как обрабатываются ваши данные комментариев.
Sha1 отпечаток ssl сертификата где взять
Once you have installed an SSL certificate on a web server or applied to a web service, you might have opened a certificate viewer or a similar tool to check if the certificate is all right, particularly if your certificate’s signature algorithm is SHA-2. You might have noticed such a thing as SHA-1 fingerprint.
In this article we will be looking at the certificate fingerprint and the certificate signature algorithm.
1. Terms checksum, hash sum, hash value, fingerprint, thumbprint are used to describe the digital output usually in a form of a hexadecimal string which is derived from a file by means of applying a hash function (algorithm) to it.
Example: 15:37:48:1E:DB:70:65:80:B2:74:E5:78:25:E5:AD:39:14:53:69:19 is the SHA-1 hash sum of ASN.1 binary (DER) form of the certificate used at www.instantssl.com.
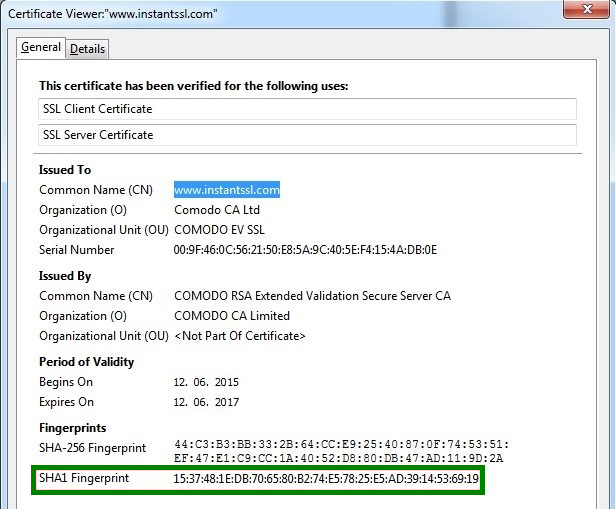
Taking fingerprint of a file presupposes putting the file through the hash sum calculation process, using a particular cryptographic hash algorithm. This is used to identify files, to facilitate certain data and security management tasks, to check data integrity against tampering or corruption. Two different files or files with a single slightest difference will produce a completely different fingerprint. Therefore, by checking and comparing certificate fingerprints webmasters and system administrators can make sure that the right file is in use.
2. Signature Algorithm field in an x509v3 SSL certificate (we provide exactly this kind of security certificates) indicates a cryptographic algorithm that is used by a Certificate Authority (CA) to sign a given certificate. By generating this signature, a CA certifies validity of the information in the certificate and the binding between the subject and the public key material in particular.
Here are the related details of the same certificate. Now we are looking at the certificate’s Signature Algorithm.
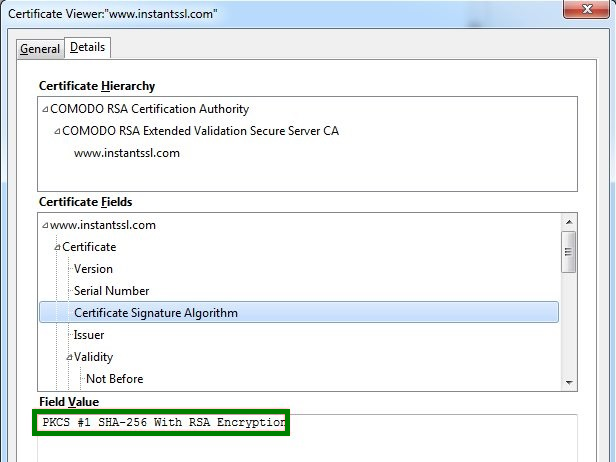
This shows that SHA-256 hash function with RSA cryptographic algorithm was used as a Signature Algorithm by Comodo CA(now Sectigo CA) to certify the connection between the public key material and the subject: Comodo CA Ltd, Salford, Greater Manchester, GB; www.instantssl.com.
At the same time, SHA-1 fingerprint was taken from the certificate to identify a larger set of information stored in the certificate itself.
The fact that we can see a SHA-1 fingerprint of a certificate in, say Mozilla Certificate Viewer, does not necessarily mean that the same cryptographic function (SHA-1) is the Signature Algorithm that was used by a Certificate Authority to issue a certificate.
This leads us to the conclusion that certificate fingerprints (MD5, SHA-1 or SHA-256 and others) are used as certificate identifiers which do not correlate with the certificate signature algorithm. The signature algorithm is encoded in a certificate and designates a cryptographic function used by a Certificate Authority to sign and issue the given certificate.
Let us remind and assure you once again that for the end-entity certificate (the one containing hostname / domain name / service hostname you apply an SSL certificate to) Comodo Certificate Authority (now Sectigo CA) uses sha256WithRSAEncryption as a default signature algorithm starting April 2014.
In order to check whether the certificate installed on your site or service was signed using SHA-1 or SHA-2 hash function family (including SHA-256), try running a quick online test or other available methods described in the “How do I check my hashing algorithm?” article in our knowledgebase.
The SHA-1 based signature algorithm sunset initiative was brought forth by major CA/Browser Forum members and software companies: Google Inc, Mozilla Foundation, Microsoft Corporation. Read on for more info on the causes and SHA-1 deprecation schedule.