Как настроить tls tunnel
TLS Tunnel
версия: 5.0.2
Последнее обновление программы в шапке: 05.06.2022


Краткое описание:
Туннелирование интернета, прокси, vpn.
TLS Tunnel использует простой протокол, который мы называем TLSVPN .
TLSVPN генерирует уникальный внутренний IP-адрес для каждого подключенного пользователя, и это позволяет устанавливать связь между пользователями на одном сервере. Эта функция является необязательной и может быть заблокирована через настройки приложения.
Весь трафик, генерируемый между клиентом и сервером, защищен протоколом TLSv1.3 .
С помощью приложения можно настроить начало соединения (мы называем это инъекцией) с набранным текстом соединения (по стандарту HTTP или любому другому стандарту) или настроить SNI для выполнения рукопожатия с сервером.
Это очень полезно для преодоления ограничений, налагаемых интернет-провайдерами или любой сетью, которую вы используете во время соединения.
Каждому пользователю присваивается идентификатор, случайно сгенерированный приложением для подключения к серверу.
Вы можете импортировать и экспортировать настройки метода подключения.
Файл конфигурации имеет расширение .tls . Это зашифрованный текстовый файл, содержащий всю информацию, которая была определена до его экспорта, за исключением DNS и параметров подключения, таких как переподключение и внутренняя защита IP .
При экспорте вы можете установить сообщение для того, кто осуществляет импорт, и заблокировать его, чтобы настройка метода не отображалась и не редактировалась.
Возможен трафик любого соединения по протоколам TCP, UDP, ICMP, IGMP.
Уважаемые пользователи!
В данной теме обсуждается лишь приложение TLS Tunnel.
Тут не обсуждаются способы обхода платы за Интернет и не сравниваются операторы мобильной связи и их тарифы.
TLS Tunneling Tool
The TLS Tunnel is a generic tool, and does things similar to stunnel, except that its driving engine is the TLS Pool. It is extensively documented on the tlstunnel(8) manual page. It can run as a client or server.
TLS Tunnel wrapping TLS around a Server
One possible use is to wrap an unprotected web server, using the TLS Tunnel to receive incoming connections with TLS, remove the TLS wrapper and forward to the plaintext web server. This can be done with
The parameters indicate:
- -s for server mode
- -l [::]:443 is the local address; in this case, it listens to all local network interfaces, specifically on TCP port 443, for incoming TLS connections
- -L testsrv@tlspool.arpa2.lab is the identity used on the local end; it represents the server over TLS
- -r [2001:db8::1234]:80 is the remote address, in this case the plaintext web server
The identities used are not very practical; they actually stem from the test setup for the TLS Pool; but you can of course insert your own; you can use identities with or without a user and @ symbol.
TLS Tunnel wrapping a Client into TLS
Another possible use of the TLS Tunnel is to take a plain text connection and wrap it into TLS. This can be done with
The parameters indicate:
- -c for client mode
- -l [::1]:8080 is the local address; in this case, it listens to localhost, specifically on TCP port 8080, for incoming plaintext connections
- -L testcli@tlspool.arpa2.lab is the local identity; it represents the client towards the server over TLS
- -r [2001:db8::1234]:443 is the remote address; it might be one of the network addresses to which the server-side TLS Tunnel from the previous section listens
- -R testsrv@tlspool.arpa2.lab is the remote identity; the client-side TLS Tunnel will validate this to authenticate the server
The identities used are not very practical; they actually stem from the test setup for the TLS Pool; but you can of course insert your own; you can use identities with or without a user and @ symbol.
Bootstrapping STARTTLS methods
An example of wrapping a web connection is a bit trivial; these connections run their TLS variants over a separate port, and will engage in the TLS handshake as soon as they are connected. Most other protocols follow a more modernised method, where they initiate in a plaintext connection, and possibly after negotiating features they will initiate a STARTTLS command. Once both ends agree to this, the TLS negotiationn starts.
The manner in which this is done differs widely across protocols. Still, the general idea is very special, and given that we know the remote endpoint we also know what exchange works for it. An example for SMTP would be:
Lines marked with S: come from the server, and C: indicates client-sent lines. Note how the server at some point indicates with a line 250-STARTTLS that it offers the facility to issue a command STARTTLS , which the client does indeed. Then, the server responds positively (with 220 whatever ) and after the end of that response the connection transcends into the TLS handshake. After having succeeded, the TLS-wrapped connection starts from scratch, because anything exchanged prior to the STARTTLS command was not protected and is thus not reliable.
The TLS Tunnel can participate in such exchanges prior to the actual TLS connection having started. To that end, it pulls an old work horse out of the meadows, namely chat(8) . In the early days of the Internet, when we used dial-in modems, we used this language to describe the stimulus/response interaction with our Internet provider’s modem pool. This was done to establish our username and password before we were allowed to start ppp and continue with IP activity.
The example script to achieve this for an SMTP server is included in the TLS Pool distribution’s extra directory; we include it here to give an idea of the type of script that can interact with a server like the one above,
Sometimes, simple solutions work best 🙂 and the result in this case is excellent: you end up having a local connection that looks like the plaintext thing, but the wrapper does everything necessary to wrap a layer of security — including this initial incarnation to get to the TLS handshake.
Limitations of a generic TLS Tunnel
The TLS Tunnel is a useful utility, especially to system administrators. But it is not a complete TLS solution, and it is important to be aware of the limitations. The generic nature of the TLS Tunnel defines both its broad usability and its inherent shortcomings.
In many applications, it is desirable to know the remote identity, so as to be able to switch behaviours. This may apply to situations with clients who identify over TLS and then are freed from the burden of manual login procedures that are run within the unreliable context of a web interface.
Note that the TLS Pool makes an effort to facilitate this mode of use; local identity selection helps to control this, the link to SteamWorks helps with remote provisioning of identities (currently a major problem to making certificates practically usable), and additional mechanisms OpenPGP, TLS-KDH, SRP #11 and additional protocols such as STARTSSH and STARTGSS help to make it ever more likely that clients can find a pragmatic technology to provide their identity over TLS.
Such identities cannot be shared from the TLS Tunnel to a plaintext client or server; the reason is simply that each of the plaintext protocols is different, and the TLS Tunnel is a generic solution. So, when the remote identity matters (or when control over the local identity is desired), the TLS Tunnel is not the best choice.
The best solution is and will always be the integration of the TLS Pool with a target application. This is why webservers have plugin modules, for example. Interestingly, it takes about an hour to add the TLS Pool to an application, and to retrieve the authenticated identities from the TLS handshake — so we provide the TLS Tunnel but really just see it as a stepping stone towards better integration with services.
Бесплатный интернет TLS Tunnel
В данной статье кратко описан механизм обхода ограничений операторов мобильной связи.
Здравствуйте, хацкеры! Прошло уже 6 месяцев с того момента, как мы заинтересовались тестированием безопасности сотовых операторов, а именно — позволит ли сайт оператора перенаправить трафик на какой-либо сервер с дальнейшим обходом фильтра.
За 6 месяцев ситуация изменилась, исправить уязвимость удалось лишь МТС, за что ей огромная благодарность, сотрудникам данной компании не зря платят. Ситуация с другими операторами потерпела немногие изменения, они так и не научились фильтровать HTTP/2.
Сегодня мы вам представляем новую инструкцию для получения бесплатного интернета при отрицательном балансе, с использованием новых технологий перенаправления трафика.
Инструкция:
- Устанавливаем на смартфон TLS Tunnel.
- Выбираем конфиг под своего оператора и нажимаем на файл (если файл не открылся в TLS Tunnel, то импортируем вручную). К сожалению, конфиг придется искать самостоятельно на просторах интернета, данные файлы больше не распространяются).
- Нажимаем «НАЧАТЬ».
Через некоторое время приложение само выберет лучший сервер и подключиться к нему, если появился ключик в строке состояния — у вас все получилось, можете пользоваться интернетом. Если же у вас ничего не появилось, то есть шанс, что со сменой порта все заработает. Также смотрите примечания под конфигами, некоторые будут работать только с определенным APN (как сменить APN ищите в Google).
Также стоит отменить, что в TLS Tunnel есть масса серверов, в том числе и RU, можете экспериментировать.
Как отключить рекламу в TLS Tunnel?
Это делается очень просто, достаточно зайти в настройки приложения и прописать первичный, вторичный DNS сервера как показано на картинке:
How to Use TLS Tunnel Application for Free Internet Tricks
Blog.Fastssh.com — How to Use TLS Tunnel Application for Free Internet Tricks — For some people, the name of the TLS Tunnel application will be very foreign to the ears. For those of you who still don’t know what TLS Tunnel is and what it’s used for, then you should listen to this article carefully.
TLS Tunnel is a VPN application that can help its users to manipulate internet connections. VPNs are widely used to help access blocked websites.
TLS Tunnel uses a simple protocol that we call TLSVPN.
TLSVPN generates a unique internal IP for each connected user, this allows the communication between users on the same server, this function is optional and can block through the app settings.
For those of you who are observant TLS Tunnel users, then you will realize that this VPN application can also be used for other things. As used for free internet tricks.
Using a VPN aims to be able to access various websites that are blocked by the government such as Tumblr. In fact, the benefits of a VPN go beyond that. Anything? Find out more by reading this article.
How to Use TLS Tunnel Application for Free Internet Tricks
Check out the tutorial below to use TLS Tunnel.
1. Download TLS Tunnel Aplication
2. Settings TLS Tunnel Aplication
There are several methods you can use on the TLS Tunnel application. Namely, Default Method, Custom Payload, Custom SNI and Custom Payload + SNI. The most frequently used ones are Custom Payload and Custom SNI.
We will explain the Custom SNI method first.
2.0.1 Settings TLS Tunnel Aplication Custom SNI method:
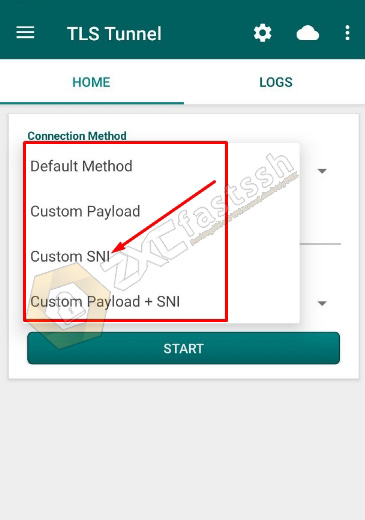
In the Connection Method, your SNI Host is filled with an active SNI host bug, for example we use SNI, .instagram.com because it will change the Instagram package to become the main quota. Then tap the logo in the upper right corner like the arrow in the image below:
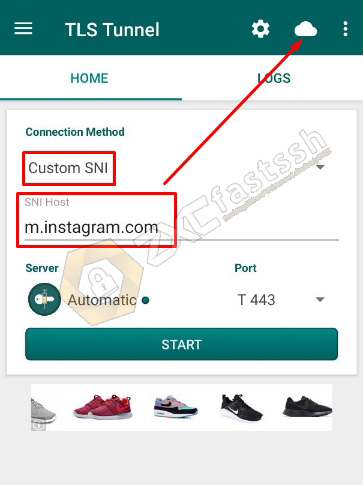
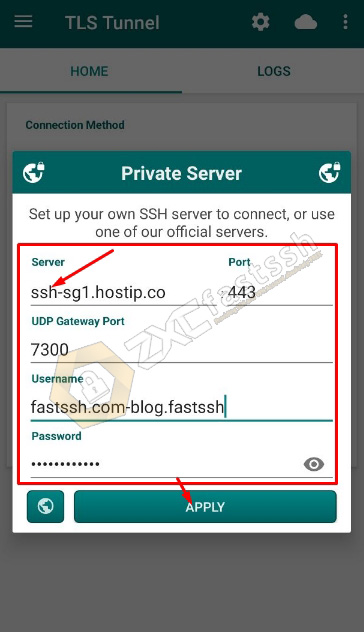
The form in the image below is the format for SSH SSL account settings. to get an SSH SSL account you can create it for free on the FastSSH.com site.
- Create SSH SSL STUNNEL TLS.
- How to Create a Free SSH Account.
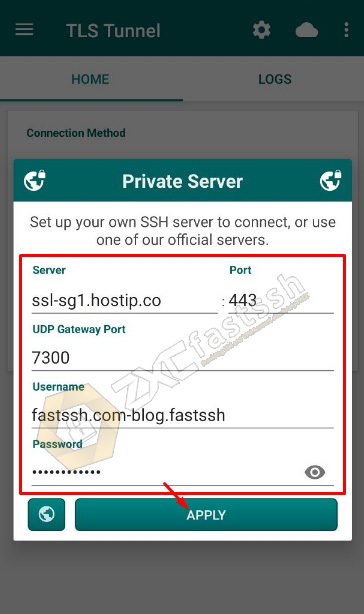
After you have successfully created an SSH SSL account, please enter the SSH SSL account that you created on the FastSSH.com site into the TLS Tunnel application as shown in the image below:
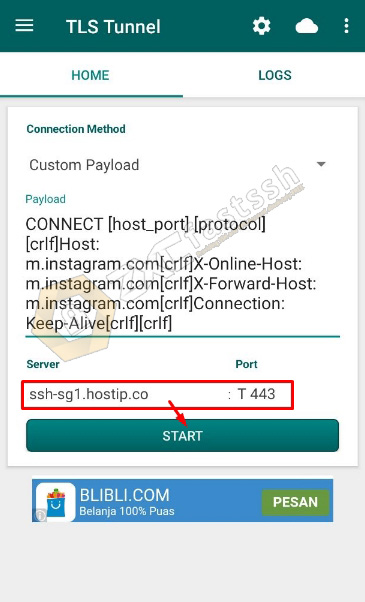
Return to the HOME menu on the TLS Tunnel application then TAP START to connect the TLS Tunnel application.
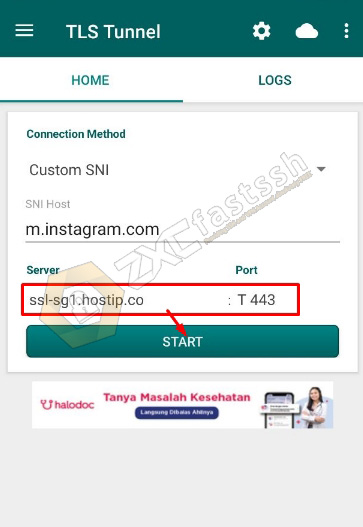
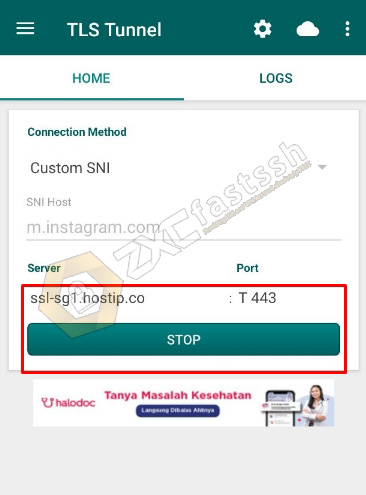
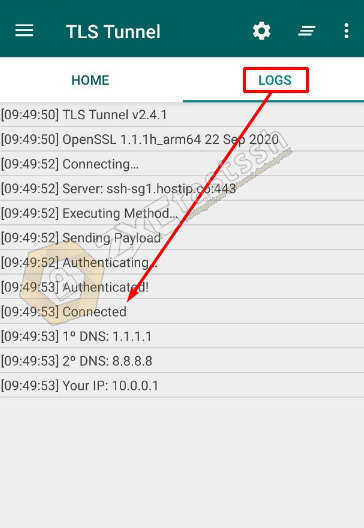
Wait a few seconds for the connection process, then tap the LOG menu to see the status whether the TLS Tunnel has successfully connected?
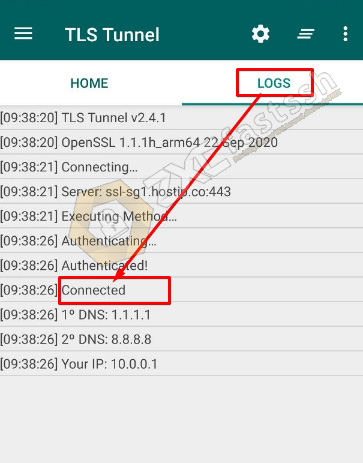
TLS Tunnel is properly connected.
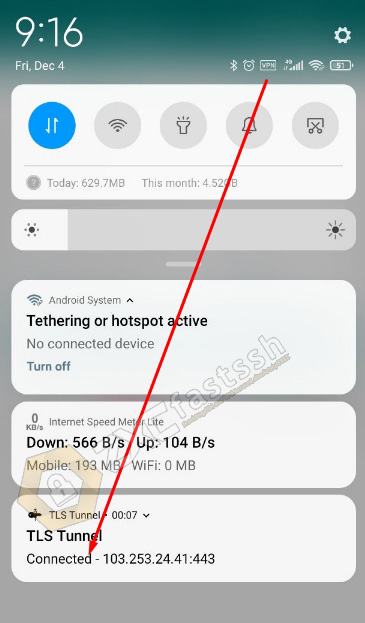
2.0.2 Settings TLS Tunnel Aplication Custom Payload method:
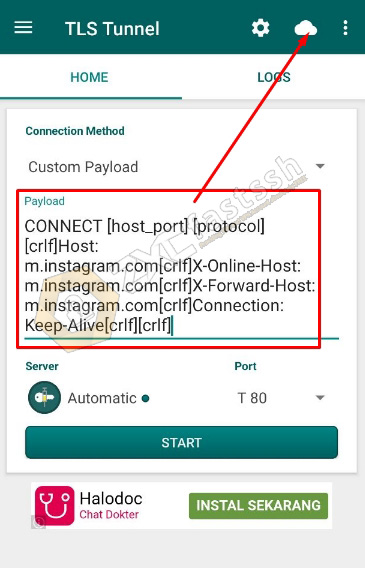
To use the TLS Tunnel with the Custom Payload method, you must use a payload that can still be active, you can change the payload according to your needs.
Select Custom Payload.
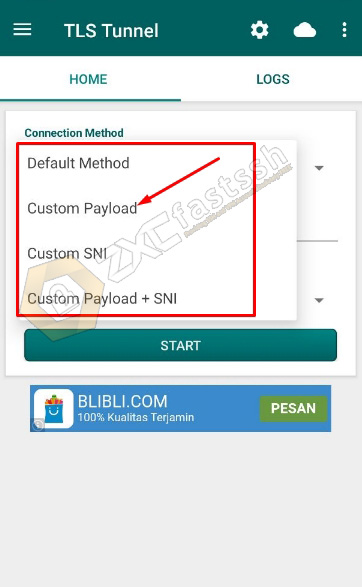
Enter your Payload. You can use the Payload below, but the Payload that we use may not work in all regions. You can create or modify it yourself.
CONNECT [host_port] [protocol][crlf]Host: m.instagram.com[crlf]X-Online-Host: m.instagram.com[crlf]X-Forward-Host: m.instagram.com[crlf]Connection: Keep-Alive[crlf][crlf]
After entering the payload, please follow the arrows for SSH settings.
- Create SSH Dropbear / OpenSSH.
- How to Create a Free SSH Account.
Tap START to Connect.
Tap LOGS to see the status.
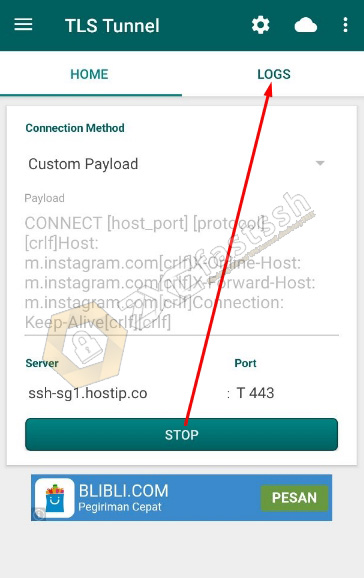
TLS Tunnel has been successfully connected properly.
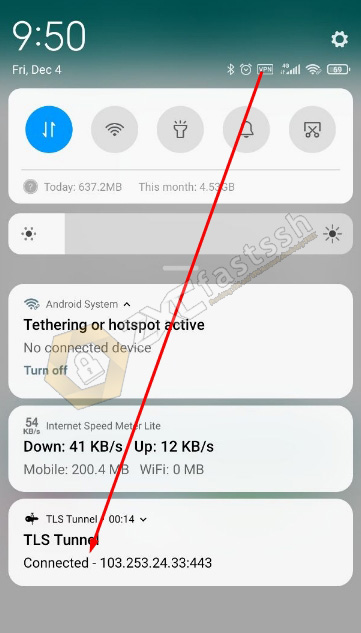
The TLS Tunnel tutorial is complete.
Conclusion
By using TLS Tunnel and using SSH, you can use it for free internet tricks and also change your ip address.