Saved searches
Use saved searches to filter your results more quickly
You signed in with another tab or window. Reload to refresh your session. You signed out in another tab or window. Reload to refresh your session. You switched accounts on another tab or window. Reload to refresh your session.
Have a question about this project? Sign up for a free GitHub account to open an issue and contact its maintainers and the community.
By clicking “Sign up for GitHub”, you agree to our terms of service and privacy statement. We’ll occasionally send you account related emails.
A gray aimclickad что за вирус
Reddit and its partners use cookies and similar technologies to provide you with a better experience.
By accepting all cookies, you agree to our use of cookies to deliver and maintain our services and site, improve the quality of Reddit, personalize Reddit content and advertising, and measure the effectiveness of advertising.
By rejecting non-essential cookies, Reddit may still use certain cookies to ensure the proper functionality of our platform.
For more information, please see our Cookie Notice and our Privacy Policy .
Get the Reddit app
Welcome To The Home Of Apps Mod Release Community Subreddit. The Only Place With Variety Of Streaming/Network/Misc/Utility Apps Collections. App's Discussion, Request, Question Everything Related Is Welcome In This Community.
A.gray.plugingame.d (Removal Guide)
A.gray.plugingame.d is the detection name for threats detected by antivirus programs. This type of threat is malicious and can do unwanted actions to the computer it infects.
Your antivirus software may have informed you of this threat because it discovered the specific malware on your computer during the program’s routine scans.
These detection warnings should not be taken lightly since it means that your device is vulnerable and can be exploited by malicious actors.
You should take appropriate actions once the anti-malware software notices these types of threats on your device. It is always best to get rid of it before it can do much harm to the computer.
These threats are often acquired through spam emails, infected websites, or by clicking on a link in an email. Once installed on the computer system, A.gray.plugingame.d will begin to spread across your PC via Windows System files.
Hackers may be able to view all the data on your computer and even take over its operation once they have been deployed on the system.
Threats like these should not be allowed to remain on the computer for an extended period because they may result in irreparable harm.
Users who have A.gray.plugingame.d on their devices are most likely to face the following problems.
- Sudden issues with internet connection and applications
- Freezing or slowdowns in computer performance
- Difficulties opening documents or accessing files.
- Pop-ups appear online or when browsing.
- Overheat and high CPU usage.
These kinds of discoveries are particularly risky since they can be used to attack unsuspecting users online by stealing their financial information, privacy passwords, and other data.
It’s critical to get rid of this particular virus as soon as you suspect you may have been impacted by it. Typically the antivirus that has detected this threat should be enough to get rid of the said malware.
Unless certain circumstances prevent the anti-malware program to eliminate the said malware, you may utilize Malwarebytes Anti Malware to help you remove the virus instead. You may follow the steps below to eliminate the threat that has been discovered in your system using Malwarebytes.
Remove A.gray.plugingame.d with Malwarebytes Anti-Malware
We have also been using this software on our systems ever since, and it has always been successful in detecting viruses. It has blocked many known computer threats as shown from our tests with the software, and we assure you that it can remove A.gray.plugingame.d as well as other malware hiding on your computer.

Not to mention, it is free to use and does not come at any cost to remove the viruses it finds on your computer.
To use Malwarebytes and remove malicious threats from the computer, follow the steps below:
1. Download Malwarebytes by clicking the button below, as we have made an additional and in-depth tutorial on how to use it. Otherwise, you may go to their official website via Malwarebytes.com (Avoid misspelling as it may lead to scams).
2. Visit their download section and start a Free Download to begin installing the software on your computer.  3. Once the Malwarebytes setup file (MBsetup.exe) has finished downloading, open the executable file in File Explorer, then right-click the setup and select run as administrator to give the highest system authority and make sure Malwarebytes is installed correctly.
 4. Make sure to carefully follow the installation setup wizard’s instructions and provide the relevant information it requires. You will be prompted with questions such as Personal or Business Use, Email Address, and others.
 5. From the application’s home screen, go to the scan tab and begin running a system scan. This will scan the whole computer, including memory, startup items, the registry, and the file system. This is done so not only the residuals of A.gray.plugingame.d but also other trojan viruses hiding in the system can be detected.
 6. Since it can take a while, you should either relax and wait for it to finish or find something else to do. The length of the scan depends on the size of the files you have and the hardware capabilities of your computer. Here are some ways to make scanning faster.
7. Once the scan is finished, Malwarebytes will show the malicious viruses and threats it found on your PC. A.gray.plugingame.d will also show up on the detection results, and it will show up in a threat name such as PUP.Optional.OpenCandy, and many more.  8. Select all the detected files from the report and click the quarantine button to remove the malicious items from the computer into the protected safe quarantine zone of the anti-malware program so that they would not affect and do malicious actions the PC again.
 9. After placing the virus files in the program’s quarantine, it may prompt you to restart the computer to finalize the full system scan procedure. Please restart your computer if prompted, as it is essential. After the restart, Malwarebytes will open and display a message that the scan was complete.
Note: Don’t forget to delete the quarantined files afterward.
Simply quarantining the malware files is not enough to make sure they are completely removed. This is a very common misconception: once you click the quarantine button, it is all good and gone.
But, while its effects and harmful activities are halted, the malware is still in the system, only placed in the anti-malware program’s quarantine folders. To completely remove it from the computer, go to Detection History from the home screen, select all Quarantined items, and click Delete.

You have successfully removed A.gray.plugingame.d as well as the hidden threats on your computer. Rest assured they would not resurface again since Malwarebytes offers a premium trial for 14 days, so you could take advantage of it for free and prevent malware from infecting your system.
While the detection and removal of malware are free for Malwarebytes, the premium versions include real-time protection that ensures your computer is safe all the time. Although we encourage you to use the premium trial, you are free to purchase the full version if you find it useful.
We suggest Malwarebytes if you are looking for a removal tool and as a second opinion scanner, but if you want full-fledged antivirus software, we believe that the built-in Windows Defender is sufficient for computer security, or if you want something with a more sophisticated system and better protection: Kaspersky Free.
If you choose to uninstall Malwarebytes, you may suddenly see that Windows Defender Real-Time Protection is turned off. This is a common issue that users may face when uninstalling the software. To fix this issue, you may refer to this article.
Alternative: Kaspersky Free Antivirus
After removing A.gray.plugingame.d and other malicious threats, you may want to install antivirus software to protect your system against malware.

More importantly, running an additional scan with a different program’s threat database will alert you to hidden Trojan viruses and rootkits that were not removed from the prior scan with Malwarebytes.Kaspersky is a widely known antivirus software that has been on the market for as long as the field of cybersecurity has existed. It is acclaimed by professionals in the field and is one of the most effective antivirus programs available. With its advanced internet security protection, it can also remove additional malware from the computer.
What is the difference between anti-malware and antivirus? Anti-Malware software is designed to specifically remove malware and its variants. In addition, it employs heuristic-based detection by picking up harmful code from files.
On the other hand, an antivirus uses signature-based detection, which examines data for attacks to protect users from dangerous viruses, including keyloggers, loaders, worms, trojans, and others.

Malwarebytes and Kaspersky are identical, but Kaspersky is a better overall program since Malwarebytes’ main purpose is to remove malware, but Kaspersky has been known for comprehensive computer security protection ever since.
Based on our experience removing malware, when two different programs are used to scan, various threats are identified by one software but not by the other. Given that their threat databases differ from each other, it might be able to capture harmful viruses, rootkits, and trojans that Malwarebytes has missed.
Please be aware that if you decide to use Kaspersky, you should first uninstall Malwarebytes because having both security programs installed will cause a conflict. If you choose to do so, please remove Malwarebytes first, as it is essential to do so before we get started.
1. Click the button below to start downloading Kaspersky Antivirus on your computer. On the following page, we have provided clear details on how to install it on the computer. On the other hand, you may go to their official website by searching for the software on your web browser or typing Kaspersky.com (Beware of misspellings since cybercriminals typically use these as exploits to redirect users to malicious webpages).
2. Go to the download page for Kaspersky Free Antivirus. Before clicking download, you will be prompted to choose your continent and where your country is located. This is very important, and you should not choose a different country because you will be met with a «Not supported in your region» message during installation.  3. Once you click download, a setup file (startup.exe) will be downloaded on the computer. After it has finished downloading, open its file location, right-click the executable file, and then select Run as administrator. This will ensure that Kaspersky’s installation will be smooth and will not result in certain errors.
 4. The Kaspersky installation wizard will launch, and you can then proceed to install Kaspersky Free by following the setup instructions. If a UAC prompt appears, simply accept it and proceed with the installation.
 5. Please be patient while Kaspersky is being installed on your computer. The speed and length of the installation process will depend on your computer’s specifications. Kaspersky also mentioned that sluggishness or dark displays during the installation of their program are normal and should not be worried about.
6. To use the antivirus program, you must first create an account on the sign-in page that appears after the antivirus application has been successfully installed on the computer. If you’re looking for the sign-up button, simply enter your email exactly as it appears; if you don’t already have an account, one will be created for you.  7. Kaspersky will ask you to decide which plan to use. It will be either the Standard version or Kaspersky Plus. In this case, the standard version is all you need for now. If you want to try the premium version of Kaspersky, you may opt for Kaspersky Plus to try the features for free. You do not have to add a payment method to get started, and after the trial ends, you will be downgraded to the Standard version unless you pay for it.
 8. You will be asked if you want to install additional applications, namely Kaspersky Password Manager and a VPN. Feel free to opt for a program you might want to use; otherwise, install both, or choose not to if you do not need them.
 9. Kaspersky will ask you to scan for viruses in the background. Simply choose not to do so because we will be doing a full system scan later; however, doing a scan now will only initiate a quick scan. However, if you want to be safe, you can run the background scan now and proceed with a full system scan after.
 10. Once the antivirus application has opened, go to the security tab and click the choose a scan button. You will be presented with several different scans; go for the full system scan to ensure full computer security. Always remember to update the database because this will ensure that Kaspersky can detect newly discovered threats and exploits.
 11. A full system scan will take a long time to finish since it will look into all the files on the computer, including the registry, memory, startup applications, and many more. The scanning time will depend on how many files there are on the computer and how big the files are. Additionally, the computer’s hardware and specs will also play into how long the scan will take.
12. After the full system scan is finished, it may detect remnants of the A.gray.plugingame.d detection virus as well as other malware hiding in the computer, showing its location along with a detection name (Trojan.Win32.Generic, Exploit.Win32.Generic, etc.) given to it. Go ahead and proceed to disinfect and restart the computer.  13. The Advanced Disinfection process will then start, and depending on the amount of RAM the computer has, it could take some time. It will then request a computer restart to complete the operation.
 Your computer will now have finished the entire system scan after restarting. By doing this, you can be sure that A.gray.plugingame.d and other types of malware and viruses have been wiped from your computer.
You shouldn’t be concerned if the scan turned up no instances of malware or viruses, which indicates that there isn’t any malware on your computer. If two independent programs declare your computer safe, then that’s probably the case.
For a better and safer web browsing experience, we’ve provided a few security measures and advice below that will safeguard your browser and computer from harmful threats like worms, malware, trojans, keyloggers, stealers, and other kinds of computer viruses that will harm user data.
Protective measures for better overall security
Removing the malicious detections from the computer is one thing; keeping it secure for the future and a long period is a different thing and will require certain things to make sure you are secured, especially if you do not know most of the ins and outs of the device you are using.
Cybercriminals are always stepping up their game to make sure they infect users and extract data and money from them.
We encourage you to take the actions listed below to ensure complete security before leaving this page because we strongly promote web security and having a secure online presence.
Safeguard your data and privacy online by using a VPN application
VPNs, also known as virtual private networks, guarantee your safety and complete anonymity while you browse the internet.
In contrast to a firewall, which monitors and blocks potentially harmful connections in the network, A VPN hides the user’s connection via a tunnel so that it would appear to third parties as a different IP address and location.
This ensures that your data won’t be leaked because the program hides it. Be aware that visiting infected websites may cause your IP address and location to be disclosed; however, if you use a VPN, this will prevent your true IP address from being revealed to malware actors.
If you already had Kaspersky installed from the previous step, you had the choice to install its integrated Virtual Private Network, which is a good tool that we also advise.
However, if you decide against doing so and instead download a VPN-only program to cloak your web browsing activity, Mullvad VPN is an excellent choice for fast connections and better privacy.

Since user privacy is the main focus of a virtual private network program, Mullvad VPN excels at putting users’ privacy first. You do not need to enter your email address while registering to download their application because they maintain anonymous accounts.
If you wanted to hide or didn’t want your credit card information to be disclosed, they also accept Bitcoin payments. According to their website, they support a free internet that is devoid of surveillance and censorship.
They have also been announcing new server locations to guarantee users a fast connection anytime they want to connect to various areas throughout the world.
Use a firewall to prevent cyber attacks
A security firewall is required for every internet connection that is made. It is an essential tool that enhances security and stops online attacks.
Through a security mechanism, it controls incoming and outgoing network connections on your system and network and filters the undesirable ones. Consider it a further barrier against malicious assaults and zero-day exploits.
You don’t need to do anything if you installed Kaspersky in the previous step because the program we installed earlier comes with a built-in firewall that is turned on by default.
On the other hand, if you prefer a standalone, fully functional firewall utility application that is exclusively focused on securing the network, we recommend ZoneAlarm Firewall.
You can also opt for ZoneAlarm Free Firewall as your first line of defense between your device and the internet. The program safeguards your network and blocks any dangers, and you can use the free version of it without paying anything.
It provides a robust two-way protection solution that guards against spyware from disclosing your data online while also hiding your PC from nefarious hackers.
With its cutting-edge anti-bot protection, it also protects your computer from automated cyberattacks in real-time.
Additionally, it protects your computer against spam, dubious websites, and many others. Lastly, it provides real-time defense against automated cyberattacks with its cutting-edge anti-bot security.
Bottom Line
Always make sure that your device is protected against sneaky exploits and stealthy cyberattacks. While taking precautions and avoiding dubious websites are crucial, having a solid line of defense is essential to ensuring the security of your network and data.
If you experience another malware issue, please visit our website to find a solution for your problem or get in touch with us, and SecuredStatus will be happy to assist you once again.
Nmmhkkegccagdldgiimedpiccmgmieda Virus
Nmmhkkegccagdldgiimedpiccmgmieda is a site-redirecting malware app that will constantly cause page-redirects in the main browser of your system with the goal to generate Pay-Per-View revenue. The main problem with irritating apps like Nmmhkkegccagdldgiimedpiccmgmieda is that they don’t always promote the safest of sites and therefore could potentially expose you to different hazards.

Many users actually have a hijacker apps like Nmmhkkegccagdldgiimedpiccmgmieda installed in their browser
It is, without a doubt, an irritating and frustrating experience to surf the online world while random advertisements are ceaselessly appearing on the screen of your computer trying to redirect you to some obscure page or to sell you some item or program. And though nowadays most sites on the Internet tend to use such adverts, banners and box-messages to boost their sales or to make extra money by promoting some other site’s items, it’s also possible that the ads in your browser are not coming from any specific site whatsoever. Many users actually have a hijacker apps like Nmmhkkegccagdldgiimedpiccmgmieda and Captcha Wizard installed in their browser which controls the browser’s search engine service, starting page and new-tab page and which also directly swarms the browser with adverts. Any browsing program could become “victim” of such hijackers – even Chrome, Firefox and Safari are not immune to that. That is why there are so many users with a browser hijacker inside of their browsing programs and, in fact, many people do not even know about it. If the symptoms we have described above are something that you, yourself, have recently been dealing with, you may need to check your browser for hijackers and then remove the unwanted software if it gets found. We already mentioned Nmmhkkegccagdldgiimedpiccmgmieda – a particularly irritating piece of software that can be regarded as a browser hijacker and inside a guide that you will see shortly, we have included removal instructions that could help our readers remove Nmmhkkegccagdldgiimedpiccmgmieda from their machines and browsers. In case you are one of the many customers with this invasive software piece in their browsers, you may want to follow the instructions as that will allow you to full uninstall the hijacker and return your main browser back to its regular state.
It is no secret that the criminals of the Internet are very good at finding different ways of reaching more and more computers with their Ransomware, Trojans, Spyware and other forms of malicious programs. One of the all time most popular tools used to achieve that are the different types of malicious adverts that they tend to spread on the Internet. This is precisely why most cyber security researchers advice the web users to keep their distance from any overly invasive online advertisements, especially if they are coming from obscure and unreliable sites. However, you can’t really be sure what the sources of the adverts that a Nmmhkkegccagdldgiimedpiccmgmieda generates are. They could be reliable and legitimate online stores but could also be shady phishing pages, obscene and sketchy sites and even sites filled with Ransomware, Spyware and other nasty infections. Because of this, you cannot trust anything a hijacker shows on your screen. This is also yet another reason why you really need to take actions towards getting rid of the pesky Nmmhkkegccagdldgiimedpiccmgmieda – it may not be a virus but it is also not a reliable app and you are strongly advised to not interact with any of the content it may spam in side your browser.
SUMMARY:
Remove Nmmhkkegccagdldgiimedpiccmgmieda Virus
To remove Nmmhkkegccagdldgiimedpiccmgmieda from your PC and the browser (or browsers) infected by it, the next steps must be compelted carefully in the order they are given:
- First, you need to make sure that you delete any recently installed programs that may be untrusted and related to the hijacker infection.
- The next task is to eradicate any rogue processes that may be shown in the Task Manager.
- Three, it’s very important to revoke any Registry, Hosts file, or Startup items list changes introduced by the hijacker.
- Finally, do not forget to remove Nmmhkkegccagdldgiimedpiccmgmieda from your browser and then clear the browser settings.
We strongly recommend that you first familiarize yourself with the detailed instructions for each of those steps that you will find down below, and only then attempt to manually delete Nmmhkkegccagdldgiimedpiccmgmieda.
Detailed Nmmhkkegccagdldgiimedpiccmgmieda Removal Guide
We recommend disconnecting the infected PC from the Internet – this can help with the hijacker removal as it will prevent Nmmhkkegccagdldgiimedpiccmgmieda from reaching out to its servers and receiving new instructions and/or resources from them.
Step 1
To remove parasite on your own, you may have to meddle with system files and registries. If you were to do this, you need to be extremely careful, because you may damage your system.
If you want to avoid the risk, we recommend downloading SpyHunter
a professional malware removal tool.
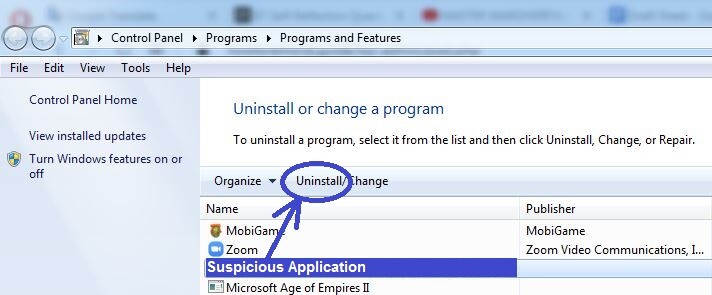
Your first task is to open the Start Menu, find and visit the Control Panel, and access its Programs and Features/Uninstall a Program section. There, look for a program that has been recently installed (around the time of the hijacker infection) and that may be related to Nmmhkkegccagdldgiimedpiccmgmieda and/or that simply looks suspicious. If such a program is visible in that list, right-click it, click the Uninstall button, and perform the uninstallation. Remember to uncheck any clauses in the uninstaller that may keep data from the program on your computer after the uninstallation.
Step 2
WARNING! READ CAREFULLY BEFORE PROCEEDING!
 We get asked this a lot, so we are putting it here: Removing a malware manually may take hours and damage your system in the process. We recommend downloading SpyHunter to see if it can detect the malware for you.
Type Task Manager in the search field below the Start Menu, open the first app and have a look at the Processes tab. If there you see an item with the name Nmmhkkegccagdldgiimedpiccmgmieda or another similar name, right-click on it, open the File Location folder of that process, then click the process, select the End Process button from the bottom-right, and confirm the action. After that, switch to the Location folder you’ve just opened, delete everything that’s in it, and then delete the folder itself.
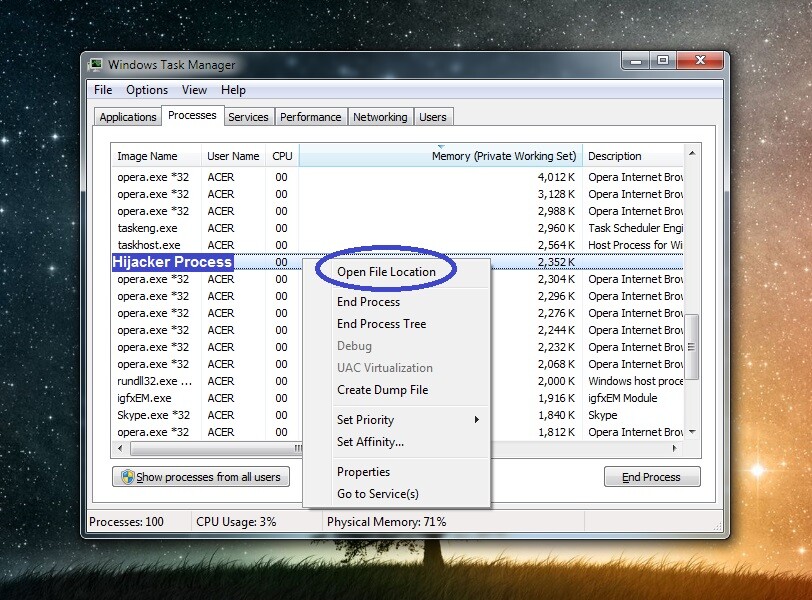
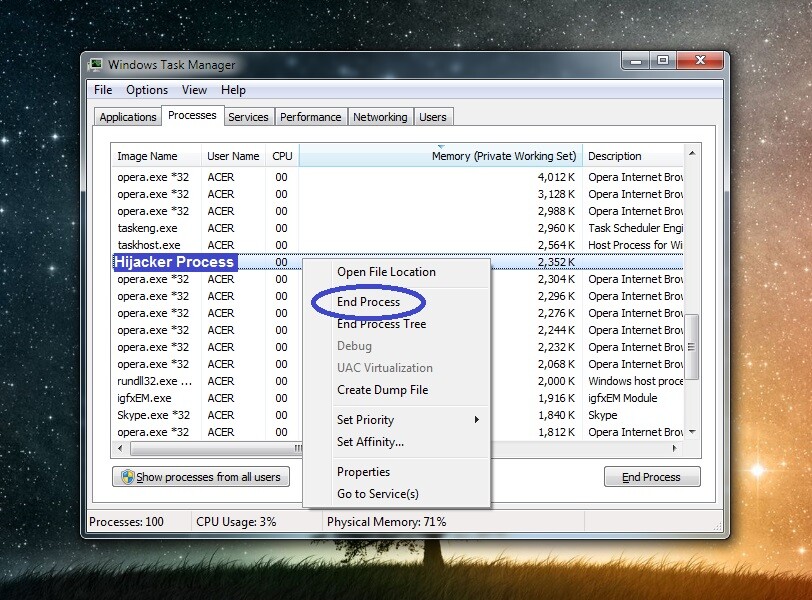
If you didn’t see a process that is named Nmmhkkegccagdldgiimedpiccmgmieda or anything similar, then look for other items with suspicious names that also have high resources usage (memory and CPU). If such processes are available in the Task Manager, use the next two methods to figure out if they are rogue and need to be stopped:
- Use Google (or another reliable search engine site) to look up the process or processes you suspect. If there are any posts on trusted security sites that say the process you suspect may be rogue, you should quit the latter and erase its location folder.
- The other thing we strongly recommend you try is to open the location folder of the process you suspect and scan everything there with the following free scanner. If it detects even one rogue file in the location folder, this means you need to get rid of the processes and its data.